A teenager from Amman, Jordan, suspected of leading the prolific and aggressive data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the Federal Bureau of Investigation (FBI) to help identify and locate other members of the notorious hacking collective.
According to reports from KrebsOnSecurity, the suspect—who operates online under the hacker handle "Rey"—was taken into custody just as ShinyHunters was actively engaged in a high-stakes extortion scheme targeting a business unit recently divested by global aerospace giant Boeing. In an ironic twist, the suspect’s father is employed by Royal Jordanian Airlines, an enterprise that relies heavily on a fleet of commercial passenger planes manufactured by Boeing.
The unfolding developments follow a Reuters report from October 3 citing three unnamed sources confirming that Jordanian authorities had detained a local individual named Saif Al-din Khader in connection with the ShinyHunters investigation. KrebsOnSecurity previously identified Rey as Khader in a November 2025 profile, during which the young man openly admitted to collaborating with multiple ransomware operations.
Rey’s name resurfaced in late September during an exclusive report regarding the Dutch police’s arrest of 24-year-old convicted cybercriminal Pepijn van der Stap. Authorities suspect Van der Stap aided ShinyHunters in carrying out various data thefts and corporate extortions. According to investigators, immediately following the Dutchman’s arrest on the evening of September 15, Rey abruptly assumed control of the ShinyHunters brand, taking to social media to publicly boast about stealing highly sensitive data from the FBI and extorting the rival Cl0p ransomware syndicate.
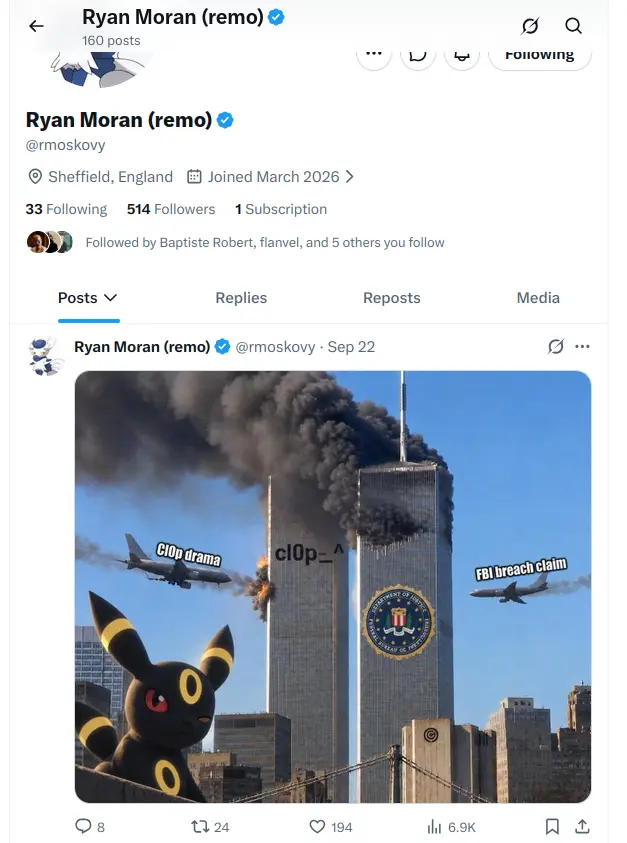
Using his long-standing account on Twitter/X, Rey taunted both federal investigators and the Cl0p operators by posting a series of custom memes. In an apparent attempt to frame Van der Stap for the breaches, Rey embedded images featuring the avatar of "Umbreon," the former hacker alias utilized by the Dutch suspect.

The security failures that enabled these attacks trace back to a critical software vulnerability cataloged as CVE-2026-35273. Discovered in Oracle’s PeopleSoft—a widely utilized software-as-a-service platform governing human resources, payroll, and recruitment administration—ShinyHunters leveraged the flaw as a zero-day exploit starting in June. Although Oracle swiftly issued a security patch, and Mandiant subsequently released specialized web application firewall (WAF) rules for organizations unable to immediately update their systems, the threat actors adjusted their methods. Hackers eventually bypassed Mandiant’s defensive rules by implementing a well-known URL-encoding evasion technique.
While ShinyHunters initially told BleepingComputer in June that their primary objective was to breach the FBI’s internal PeopleSoft database—an attempt that reportedly failed—subsequent mass exploitation campaigns yielded significant results. A joint threat intelligence report published on September 25 by Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that the syndicate successfully harvested data from dozens of enterprise systems across diverse sectors, including higher education, technology, healthcare, agriculture, transportation, and government agencies.
Further compounding the fallout, Reuters reported on October 5 that the FBI had dismissed an Accenture contractor following revelations that a failure to properly patch the bureau’s recruitment portal directly enabled the ShinyHunters breach. That security failure exposed sensitive records belonging to over 5,000 FBI personnel, detailing specific operational units, specializations, and confidential medical and psychiatric files.
"Rey" Means King, as in Royal
Investigators close to the ongoing multi-jurisdictional inquiry revealed that a digital aviation and navigation unit recently divested by Boeing was directly in the crosshairs of ShinyHunters’ extortion demands at the time of Rey’s apprehension. The syndicate’s attempt to pressure the former Boeing subsidiary alarmed federal investigators, given that the stolen proprietary datasets posed significant operational safety and security risks.
In a brief official statement addressing the incident, Boeing acknowledged being aware of the extortion attempts linked to data stolen from Jeppesen ForeFlight. Boeing previously sold the subsidiary in November 2025 to private equity firm Thoma Bravo for approximately $10.55 billion.

"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson noted, adding that the company is actively reviewing the situation alongside the Jeppesen ForeFlight team. Meanwhile, representatives for Jeppesen ForeFlight maintained that their internal investigation found no operational disruption or compromise of products.
Rey’s alleged involvement in targeting the aviation unit draws heightened scrutiny given his family connections. Evidence indicates his father works for Royal Jordanian Airlines, a carrier majority-controlled by the Jordanian government that operates long-haul aircraft built by Boeing. While Rey claimed on Telegram in early 2025 that his father worked as an airline pilot, those claims remain unverified. However, forensic analysis of a password-stealing malware infection on the family’s shared computer revealed that Rey’s father utilized identical credentials across multiple administrative portals designated for Royal Jordanian Airlines employees.
Royal Jordanian Airlines has not responded to requests for comment regarding the security compromise. Prior to publishing their late September investigations, security researchers attempted to contact Rey’s father to provide updates on his son’s illicit activities. Although neither family member responded, Rey began purging his online presence within hours of the outreach, deleting various social media profiles, including the Twitter/X account used to taunt law enforcement and corporate victims.
Despite scrubbing most of his accounts, Rey’s cybersecurity blog hosted on GitHub remained active. A lengthy post published on the blog in March 2026 unmasked two Russian nationals, identifying them as the core developers and masterminds behind the Cl0p ransomware operation.
Murder for Hire Allegations
While authorities press forward in Jordan, legal proceedings in the Netherlands have introduced far more sinister allegations against Pepijn van der Stap. Despite widespread media coverage portraying the young cybercriminal as a reformed hacker who had successfully transitioned into a legitimate security career, Dutch daily newspaper RTL reported on September 29 that investigators suspect Van der Stap of orchestrating at least two murders. According to prosecutors, the intended attacks were planned to take place abroad, and investigators have gathered indications that Van der Stap issued direct orders for the hits.

Van der Stap was previously released from prison after completing the majority of a four-year sentence for data theft and extortion crimes that netted an estimated 1.5 million to 2.7 million euros. During a September 9 interview, Van der Stap claimed he was working as an "offensive security lead" at Neo Security, a Dutch cybersecurity firm where his responsibilities ostensibly involved testing client networks for vulnerabilities.
Benjamin Korper, the owner of Neo Security, told Reuters that he retained an external auditing firm to investigate whether Van der Stap had compromised the company or its clients. Thus far, independent investigators have uncovered no evidence of internal malicious activity. However, Korper confirmed that Dutch forensic teams raided his corporate offices on the night of September 15, executing an operation that reportedly utilized flash-bang grenades to apprehend Van der Stap.
Before his initial arrest in 2023, Van der Stap maintained a dual life as a software engineer for Amsterdam-based cybersecurity startup Hadrian and as a volunteer for the Dutch Institute for Vulnerability Disclosure (DIVD), all while orchestrating ransomware attacks and data extortion schemes against major international targets. When questioned about how the public or victims could trust a self-described reformed criminal who had successfully deceived colleagues and journalists alike, Van der Stap maintained that his actions would ultimately speak for themselves.
Franchising and Burning a Brand
Cybercriminals operating under the ShinyHunters banner have been linked to dozens of massive data breaches compromising billions of records in campaigns stretching back to 2019. However, cybersecurity experts emphasize that the individuals currently wielding the ShinyHunters moniker bear little relation to the group’s original core members, most of whom are French nationals who have previously faced arrest and imprisonment.
Instead, ShinyHunters has evolved into an amorphous franchise model. Security analysts compare the structure to the fictional "Dread Pirate Roberts" from the classic film The Princess Bride, where succession is determined by law enforcement arrests rather than death, allowing multiple individuals to operate under the same legendary alias simultaneously. Federal investigators are increasingly focusing on a network of freelance affiliates who feed stolen SaaS platform credentials to whoever controls the brand in exchange for a percentage of any successful ransoms.

In the wake of Van der Stap’s arrest, chat servers on Telegram allegedly managed by Rey became hotbeds of internal conflict. Community members openly ridiculed Rey after he capitulated on threats made against the FBI and Cl0p, a humiliation compounded when the primary ShinyHunters darknet extortion portal abruptly went offline. Critics within underground forums accused Rey of buying legacy cryptographic keys and larping as ShinyHunters solely to monetize stolen data and boost his personal profile.
A rival Telegram channel tracking the underground community has spent weeks doxing and harassing alleged ShinyHunters members, portraying Rey as an inexperienced amateur attempting to exploit a burnt cybercriminal brand. According to channel administrators, Rey’s decision to co-opt the dismantled group’s name while launching independent extortion schemes ultimately led to his downfall.
The group’s operational strategy had previously drawn direct confrontation from federal authorities. In a formal flash notice issued on May 15, the FBI warned organizations against paying ransoms to ShinyHunters, detailing the syndicate’s aggressive harassment tactics. These methods historically included bombarding corporate victims and their relatives with threatening phone calls and text messages, engaging in physical swatting incidents, and fabricating claims regarding the possession of sensitive personal media.
In interviews with tech publications following the FBI’s advisory, representatives for ShinyHunters argued that their decision to target the bureau was designed to counter official agency warnings and reassert their technical capabilities. At the same time, the hackers conceded that the government’s public awareness campaign significantly damaged their leverage, acknowledging that the high-profile attacks served primarily as a desperate public relations maneuver to salvage their extortion enterprise.