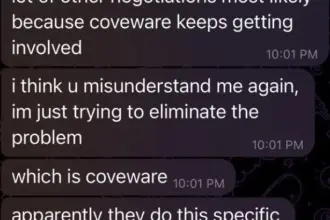
Federal Bureau of Investigation agents have arrested a prominent executive at a Canadian cybersecurity firm in connection with an intensifying, high-stakes investigation into the notorious "ShinyHunters" cybercrime syndicate. The arrest comes on the heels of a massive security breach that saw the hacking group infiltrate federal networks and make off with sensitive personnel data belonging to thousands of law enforcement agents.
According to multiple sources speaking with KrebsOnSecurity, the individual was taken into custody while visiting Pennsylvania to attend a prominent cyber insurance and risk management convention. The New York Times was first to report that federal authorities had arrested a Canadian man in Pennsylvania on suspicion of providing assistance to the ShinyHunters operation. While neither The Times nor a public statement published on social media platform X by FBI Director Kash Patel identified the suspect by name, a clearer picture of the detention has since emerged through federal court filings, conference disclosures, and industry sources.
One source close to the ongoing federal inquiry revealed that the Canadian executive was in the United States to participate in the Cyber Risk Summit, a specialized industry gathering held at the Loews Philadelphia Hotel. The suspect’s professional background is deeply rooted in the niche sector of handling ransomware negotiations and cyber extortion advisory services for corporate and institutional clients. Sources familiar with the broader case also indicated that day-to-day operational control and oversight of the ShinyHunters investigation have recently been centralized at a major FBI field office in Texas, reflecting the sprawling and multi-jurisdictional nature of the federal response.
Publicly available records and conference listings indicate that the Cyber Risk Summit took place between October 5 and October 7. Among the numerous sponsors supporting the summit, event documentation shows that the single largest corporate sponsor was a prominent Canadian security firm named Cypfer.
Further digital footprint analysis reveals that an individual named Edward Dubrovsky was previously linked to Cypfer. According to historical LinkedIn data, Dubrovsky was listed as a co-founder of the firm before moving on to another Canadian security organization and summit sponsor known as CyberSteward. Approximately one month prior to his arrest, Dubrovsky shared a post on LinkedIn announcing his travel plans to attend the Cyber Risk Summit alongside his colleagues from the CyberSteward team, expressing enthusiasm for continuing industry dialogues regarding global ransomware advisory, settlement strategies, and extortion negotiations.

In the wake of the news, a corporate spokesperson for Cypfer clarified that Dubrovsky was never a founder or co-founder of the company, as his LinkedIn profile had claimed, but rather served in the capacity of a managing director prior to his resignation from the firm in November 2025.
Federal court records filed in Pennsylvania point directly to the unfolding legal proceedings. On October 8, an individual named Edward Dobrovsky—noting a slight spelling variation in the surname—was taken into custody on charges related to cyber extortion and criminal conspiracy. While several key documents, including the foundational criminal complaint, have been placed under seal by the court, a handful of related filings were indexed on CourtListener.com. These accessible documents include a summary of the complaint, which formally charges the defendant with "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats."
Inmate locator records maintained by the U.S. Bureau of Prisons indicate that a 54-year-old Edward Dubrovsky is currently being housed at a federal detention facility in Philadelphia. However, court docket entries show that a transfer notice was filed on October 9 moving the case jurisdiction to the U.S. District Court for the Eastern District of Texas, aligning with reports that Texas has become the central hub for the government’s comprehensive ShinyHunters probe. Officials with the FBI have declined to comment on the specifics of the ongoing prosecution.
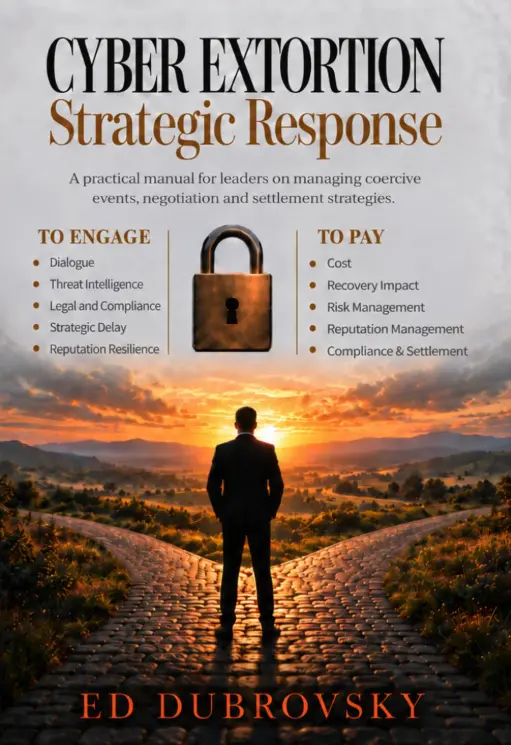
Beyond his executive roles in the cybersecurity sector, Dubrovsky is the author of a 252-page book titled Cyber Extortion Strategic Response, which purports to guide organizations through the complex decision-making processes required to survive and recover from digital ransom demands. Promotional materials for the publication emphasize the author’s philosophy regarding the nuances of criminal extortion, asserting that communication with cybercriminals is distinct from negotiating a payout, and that engagement can serve tactical purposes such as verifying claims, buying time, and preserving institutional options.
At the time of reporting, legal representation for Dubrovsky had not yet been formally established, and court records show he has yet to be assigned a public defender. Representatives for CyberSteward have not yet issued a public statement regarding the arrest of their executive.
The ShinyHunters hacking group has established a formidable and destructive reputation in the global threat landscape by utilizing sophisticated phishing campaigns and stolen credential harvesting to breach corporate software-as-a-service accounts. Once inside corporate networks, the syndicate routinely exfiltrates vast repositories of proprietary and confidential data, threatening to leak the information publicly unless exorbitant ransom demands are satisfied. According to federal estimates, the criminal collective has successfully extorted more than $70 million from corporate and institutional victims over the course of the year.

The arrest of the Canadian executive is part of a much broader, highly accelerated international law enforcement crackdown on the infrastructure and associates supporting ShinyHunters. Investigators have been meticulously reviewing digital evidence and electronic devices seized last month by European authorities. Those seizures followed an operation by the Dutch police resulting in the arrest of Pepijn van der Stap, a reformed hacker suspected of playing a key role in the network. Sources indicate that these evidentiary reviews could soon yield additional criminal charges against principals at other firms operating within the high-stakes ransomware negotiation ecosystem.
The pressure on the hacking syndicate has sparked an aggressive and public retaliation campaign from within the group’s leadership. Immediately following the apprehension of Van der Stap, another prominent member of ShinyHunters operating under the alias "Rey" assumed control of the group’s operations. This new faction leader quickly began taunting federal investigators online, boasting about a high-profile breach that compromised sensitive data from the FBI’s own online recruitment portal. The stolen material reportedly included detailed personnel information, unit assignments, professional specializations, and confidential medical and psychiatric records of prospective and active agents.
Law enforcement efforts culminated in international cooperation that led to the identification and detention of the individual operating behind the alias "Rey." Reuters reported that the suspect, identified as a teenager named Saif Al-din Khader, had been detained and was actively cooperating with federal investigators. The apprehension occurred as the cybercrime collective attempted to extort a prominent navigation and digital aviation unit that had been divested by aerospace giant Boeing in late 2025.
As federal authorities continue to untangle the web of co-conspirators, negotiators, and digital extortionists tied to the ShinyHunters network, the investigation remains an active and rapidly evolving national security priority.