Federal Bureau of Investigation agents have arrested a high-profile executive from a Canadian cybersecurity firm in Pennsylvania, marking a dramatic escalation in the ongoing, high-stakes federal investigation into the notorious ShinyHunters cybercrime syndicate. The arrest comes on the heels of a massive digital breach that saw the hackers successfully siphon sensitive personal and professional data concerning thousands of FBI agents from the bureau’s internal systems.
According to multiple sources familiar with the ongoing probe, the federal operation has increasingly zeroed in on individuals and entities operating within the specialized ecosystem of ransomware negotiations and cyber extortion response. Court records and investigative reporting indicate that the suspect was apprehended while visiting the United States to attend a prominent cybersecurity and cyber insurance conference in Philadelphia.
The New York Times first reported the arrest of the Canadian man on suspicion of providing illicit assistance to the ShinyHunters organization. While neither the initial reports nor an official social media statement released by FBI Director Kash Patel initially named the individual, subsequent federal court filings and investigative sources confirmed the identity of the detained executive as 54-year-old Edward Dubrovsky.
Dubrovsky is a well-known figure in the digital security industry, a veteran practitioner of ransomware response, and the author of a comprehensive book examining the complex mechanics of cyber extortion. Federal court documents show that an individual under the slightly misspelled name Edward Dobrovsky was taken into custody on October 8, facing serious federal charges including conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.
A High-Stakes Arrest at a Cyber Risk Summit
According to sources close to the investigation, Dubrovsky had traveled to Pennsylvania to participate in the annual Cyber Risk Summit, an industry gathering held at the Loews Philadelphia Hotel between October 5 and October 7. The conference brought together a broad cross-section of cyber insurance professionals, legal experts, and incident response firms. Publicly available event sponsorship records indicate that the summit’s largest corporate sponsor was Cypfer, a prominent Canadian security company specializing in ransomware management and negotiation.
Online professional profiles indicate that Dubrovsky was historically associated with Cypfer, though representatives for the firm later clarified his exact corporate lineage. In an official update provided to reporters, a Cypfer spokesperson stated that Dubrovsky was never a founder or co-founder of the organization, as his professional networking profile had previously claimed, but instead served as a managing director prior to his resignation in November 2025. Following his departure from Cypfer, Dubrovsky became affiliated with CyberSteward, another Canadian security firm and conference sponsor, and had publicly advertised his intention to attend the Philadelphia summit alongside his new team.

In a professional post published to social media roughly one month prior to his arrest, Dubrovsky expressed enthusiasm for continuing industry conversations regarding strategic advisory, negotiations, and global settlement services concerning coercive cyber incidents, such as ransomware and data extortion. Ironically, federal prosecutors now allege that his involvement with the underworld of cyber extortion extended far beyond advisory roles and lawful negotiations.
Shifting Jurisdictions and Growing Federal Scrutiny
Following his apprehension by FBI agents, Dubrovsky was initially booked and held at a federal detention facility in Philadelphia, as reflected in inmate locator data maintained by the U.S. Bureau of Prisons. However, court records indexed at CourtListener.com reveal that the case was swiftly transferred via a judicial notice filed on October 9 to the Eastern District of Texas. Multiple sources indicate that this federal district has quietly become the central command hub and primary epicenter for the comprehensive nationwide investigation into the ShinyHunters infrastructure.
Available court documents in the case remain heavily restricted, with the core criminal complaint and several accompanying exhibits placed under seal by the court. Available docket entries show that Dubrovsky has yet to secure private legal counsel or be formally assigned a public defender by the court system. Representatives for the FBI have consistently declined to comment on the ongoing prosecution, citing the active nature of the multi-jurisdictional sweep.
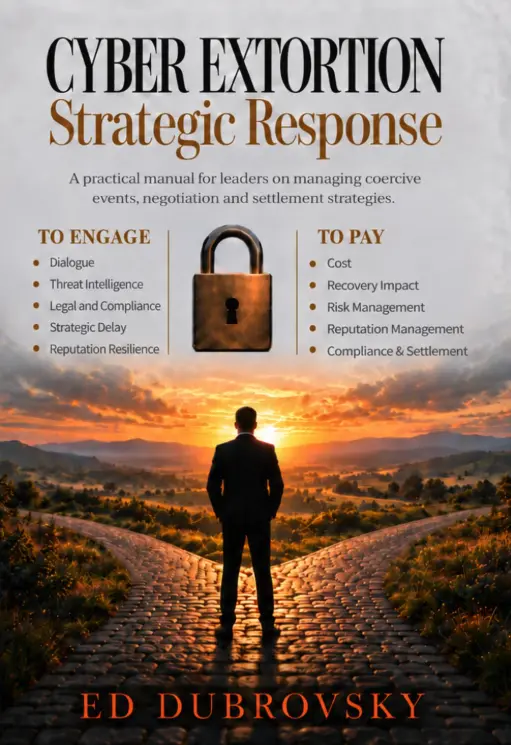
Dubrovsky’s public footprint within the cybersecurity industry heavily emphasized the intricate gray areas of digital extortion response. His published 252-page work, Cyber Extortion Strategic Response, was marketed as a definitive guide designed to take corporate leaders beyond the initial shock of a ransom note and into the strategic decision-making processes required during an active crisis.
Excerpts from the book’s promotional materials underscored a central thesis taught by many incident response professionals: that active communication with cybercriminals does not inherently equate to negotiating a monetary payment, and that opening channels of dialogue can serve tactical objectives such as verifying attacker claims, buying time, and preserving options while an organization evaluates its defensive posture. Federal investigators now intend to prove that the boundaries between lawful advisory work and criminal facilitation were allegedly crossed.
The Expanding Scope of the ShinyHunters Investigation
The dramatic arrest of the Canadian cybersecurity executive underscores the intense pressure facing federal law enforcement as they grapple with the fallout from the ShinyHunters campaign. The cybercriminal collective has established a formidable reputation for executing sophisticated phishing campaigns and systematically compromising corporate user accounts at major software-as-a-service providers. Once inside corporate networks, the group exfiltrates vast repositories of sensitive data and subjects victims to aggressive extortion demands, threatening to leak proprietary information publicly unless substantial cryptocurrency ransoms are satisfied. According to internal law enforcement assessments cited by the FBI, the syndicate has successfully extracted upwards of $70 million from corporate and institutional victims over the course of the year.

The dragnet closing around ShinyHunters has accelerated significantly over the past several weeks. Law enforcement agencies have been exhaustively analyzing digital devices and hardware seized last month when Dutch police successfully apprehended Pepijn van der Stap, a reformed cybercriminal linked to the hacker collective, during a coordinated international operation. Sources indicate that as federal prosecutors pore over the recovered forensic evidence, additional criminal charges against high-ranking principals at other commercial firms specializing in ransomware mitigation and negotiation may be imminent.
The urgency within the FBI has been amplified by the brazen behavior demonstrated by the hackers following Van der Stap’s capture. Immediately after the Dutch police operation, a prominent individual within the syndicate operating under the online pseudonym "Rey" seized operational control of ShinyHunters. This new leadership figure began openly taunting federal investigators, publicly boasting about a catastrophic breach of the FBI’s own online recruitment portal. The stolen cache reportedly contained highly sensitive background details on thousands of job applicants and active personnel, including unit assignments, professional specializations, and confidential medical and psychiatric records.
International law enforcement collaboration ultimately closed the net on the online persona known as Rey. Investigative reporting by Reuters identified the individual as a teenager named Saif Al-din Khader, who was subsequently detained by authorities and is reportedly cooperating with federal investigators. Security analysts detailed how Khader was tracked down as the cybercrime group attempted to execute an aggressive extortion campaign against a digital aviation and navigation unit recently divested by aerospace giant Boeing.
As federal agents continue to untangle the complex web of facilitators, negotiators, and hackers that sustained the ShinyHunters enterprise, legal proceedings in Texas and Pennsylvania are expected to move swiftly, shedding further light on the shadowy intersection where corporate cyber defense and digital extortion meet.