A teenager from Amman, Jordan, suspected of leading the prolific data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the FBI to identify other members of the hacking collective.
According to reports from KrebsOnSecurity, the suspect—who uses the hacker handle “Rey”—was apprehended just as ShinyHunters was in the middle of an aggressive campaign to extort a business unit recently divested by global aerospace giant Boeing. In a striking twist of geographical coincidence, the target of the extortion shares an indirect connection to the suspect’s home life: Boeing manufactures the fleet of aircraft utilized by Royal Jordanian Airlines, the employer of Rey’s father.
On October 3, Reuters cited three unnamed sources confirming that a suspected ShinyHunters member in Amman named Saif Al-din Khader had been detained by Jordanian authorities and was actively assisting the FBI. KrebsOnSecurity previously identified Rey as Khader in a November 2025 profile, during which the young man admitted to collaborating with multiple ransomware operations.
Rey re-emerged in the headlines in a September 28 exclusive detailing the arrest of 24-year-old convicted Dutch cybercriminal Pepijn van der Stap, whom Dutch police apprehended on suspicion of assisting ShinyHunters with data thefts and extortions. Security investigators noted that immediately following the Dutchman’s dramatic arrest on the evening of September 15, Rey seized control of the ShinyHunters brand, publicly boasting about breaching the FBI and extorting the notorious Cl0p ransomware group.
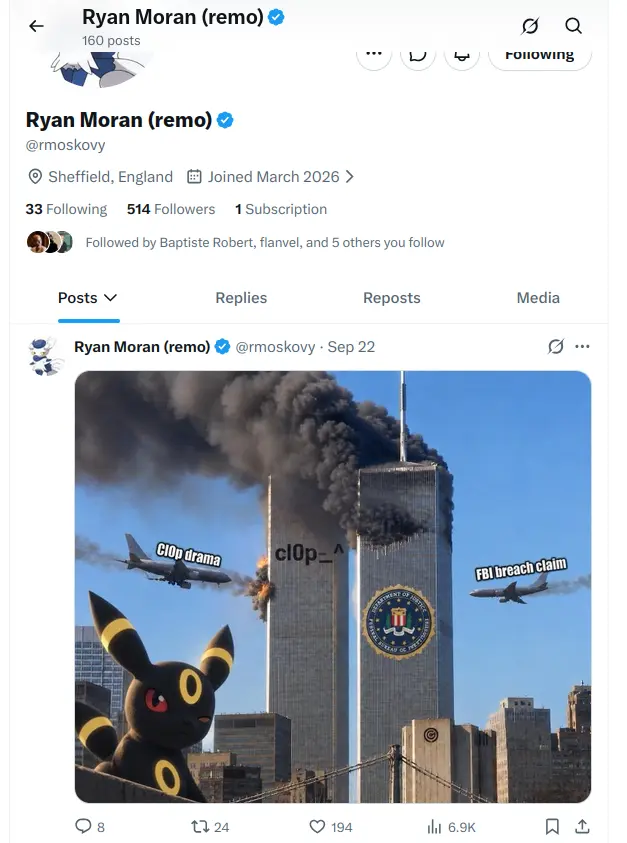
Using his longtime account on Twitter/X, Rey taunted both the FBI and Cl0p with a series of memes while deliberately incorporating images of the avatar used by Van der Stap’s former hacking alias, “Umbreon.” Investigators believe this was a calculated maneuver intended to frame the Dutch national for the high-profile hacks.
The campaign that enabled these breaches traced back to the exploitation of a critical security flaw (tracked as CVE-2026-35273) in PeopleSoft, a software-as-a-service platform developed by Oracle that is widely deployed across enterprises for human resources, payroll, and benefits management. Oracle quickly issued a patch after ShinyHunters began weaponizing the vulnerability as a zero-day in June. Simultaneously, cybersecurity firm Mandiant released web application firewall (WAF) rules for organizations unable to immediately apply the security update.

While ShinyHunters originally told BleepingComputer in June that their initial objective was to breach the FBI’s own PeopleSoft database—an attempt they claimed was unsuccessful at the time—the group later bypassed Mandiant’s defensive measures using a well-known URL-encoding trick. In a September 25 joint advisory, experts from Mandiant and the Google Threat Intelligence Group confirmed that ShinyHunters had mass-exploited the PeopleSoft vulnerability, compromising dozens of systems across higher education, technology, healthcare, agriculture, transportation, and government sectors.
Further compounding the fallout, Reuters reported on October 5 that the FBI dismissed an Accenture contractor over failures to patch the agency’s recruitment website. The ShinyHunters breach of that portal exposed sensitive records belonging to more than 5,000 FBI personnel, including unit assignments, specializations, and confidential medical and psychiatric records.
‘Rey’ Means King, as in Royal
According to two sources familiar with the ongoing international investigation into ShinyHunters, a digital aviation and navigation unit divested by Boeing was among the primary targets being extorted by the group when Jordanian law enforcement moved in to arrest Rey.
The investigation into the syndicate gained significant momentum following the attempted shakedown of the former Boeing division. Sources indicated that the stolen data involved sensitive operational details that could potentially introduce serious aviation safety and security risks.
In a brief statement, Boeing acknowledged the extortion attempts directed at data originating from Jeppesen ForeFlight, a subsidiary that Boeing sold in November 2025 to private equity firm Thoma Bravo for $10.55 billion.
"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson said, adding that the company was actively reviewing the incident alongside the Jeppesen ForeFlight team. A spokesperson for Jeppesen ForeFlight maintained that their internal investigations found no operational impact, stating that their proactive security posture protected their products and core operations.

Rey’s alleged role in targeting the former Boeing unit carries personal irony given his family ties. Evidence indicates his father is employed by Royal Jordanian Airlines, a carrier majority-controlled by the Jordanian government that operates long-haul flights using Boeing aircraft. While Rey claimed on Telegram in early 2025 that his father worked as an airline pilot, that specific detail could not be independently verified.
However, forensic data from a password-stealing malware infection on the family’s shared computer showed that Rey’s father routinely used identical login credentials across multiple administrative portals for Royal Jordanian Airlines employees.
Royal Jordanian Airlines did not respond to requests for comment. Shortly before publishing a September profile update, KrebsOnSecurity reached out to Rey’s father regarding his son’s activities. Within hours of that outreach, Rey began scrubbing his digital footprint, systematically deleting social media accounts, including the Twitter/X handle used to taunt the FBI and Cl0p.
Despite purging his social profiles, Rey’s cybersecurity blog hosted on GitHub remained online. A lengthy March 2026 post on the blog unmasked two Russian men alleged to be the core developers and masterminds behind the Cl0p ransomware operation, effectively doxing the leadership of one of the cybercrime underground’s longest-running extortion rings.
Murder for Hire Allegations
As the investigation into the digital underground deepens, Dutch media outlets have surfaced explosive new allegations against Van der Stap, whose narrative of personal rehabilitation following a prior conviction had previously won over portions of the tech press. The Dutch daily RTL reported on September 29 that investigators suspect Van der Stap of orchestrating at least two murders intended to be carried out abroad.
Van der Stap had recently completed the majority of a four-year prison sentence for data theft and extortion activities that prosecutors estimated yielded between 1.5 million and 2.7 million euros. During a September 9 interview, Van der Stap maintained he was working as an "offensive security lead" for Neo Security, a Dutch cybersecurity firm where his responsibilities supposedly included testing client networks for vulnerabilities.

Neo Security owner Benjamin Korper told Reuters that he hired an independent third-party firm to audit his company for any signs of internal compromise by Van der Stap. Investigators reportedly found no evidence that the suspect targeted his employer or its clientele. Korper confirmed that Dutch forensic officers raided his office on September 15, the same night Van der Stap was captured by a specialized police intervention unit utilizing flash-bang grenades.
Prior to his initial 2023 arrest, Van der Stap worked as a software engineer at Amsterdam-based cybersecurity startup Hadrian and volunteered with the Dutch Institute for Vulnerability Disclosure, all while participating in clandestine hacking and extortion operations against major corporate targets. When questioned about how the public could trust a self-described reformed hacker who deceived colleagues and journalists alike, Van der Stap expressed resignation.
"You can throw a bunch of nice words at someone, but you can’t convince them if they don’t want to be convinced," Van der Stap said. "I’m doing what I can to repay victims, and that’s all I can do."
Franchising and Burning a Brand
Cybercriminals operating under the ShinyHunters banner have been linked to dozens of major data breaches accounting for billions of stolen records, with activities tracing back to at least 2019. Security experts emphasize, however, that the individuals controlling the name today bear little resemblance to the group’s original French core members, many of whom have previously faced arrest and imprisonment.
Instead, ShinyHunters has evolved into a criminal franchise. Law enforcement sources compare the structure to the fictional Dread Pirate Roberts from The Princess Bride, where succession occurs through arrest rather than death, allowing multiple individuals to operate under the same legendary moniker simultaneously. Current FBI investigations are largely focused on a network of freelance cybercriminals who feed stolen corporate credentials into the hands of operators in exchange for a percentage of subsequent ransom payments.
In the wake of Van der Stap’s arrest, private Telegram channels operated by Rey became battlegrounds for ridicule. Fellow underground members mocked Rey after he retreated from his public threats against the FBI and Cl0p, and as the main ShinyHunters darknet portal abruptly went offline following an FBI ultimatum. Commentators accused the teenager of purchasing legacy forum encryption keys and hijacking the defunct brand to run extortion scams for personal profit.

A competing Telegram channel known as "The Battle" dedicated weeks to doxing and criticizing Rey and his associates, characterizing him as an inexperienced novice riding the coattails of an infamous name.
"Rey made a serious mistake when he started pretending to be a member of ShinyHunters," the administrators of The Battle wrote. "That group had already been dismantled… yet Rey still chose to use its name while carrying out his crimes."
In a separate interview with The Register, representatives for ShinyHunters claimed their decision to target the FBI was a retaliatory public relations move designed to counter an agency flash notice issued in May. That FBI warning advised victims against paying ransoms to the group and detailed aggressive tactics utilized by its affiliates, ranging from harassing phone calls and text messages to swatting incidents and the false posturing of possessing compromising personal media.
While the hackers asserted that their breach of the bureau demonstrated their technical prowess, leadership within the collective ultimately acknowledged that the FBI’s public warnings severely damaged their extortion prospects, conceding that the digital war of words had evolved into a high-stakes battle over marketing and public perception.