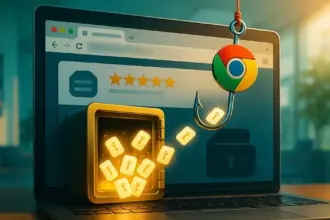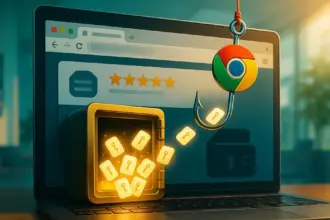
For a few critical days in November, a sophisticated and malicious Chrome extension managed to climb the ranks of the Chrome Web Store, briefly securing the fourth position for the heavily searched term "Ethereum wallet." Posing as a legitimate tool under the name "Safery: Ethereum Wallet," the application bypassed automated checks and deceived users with a polished frontend, clean iconography, a generic security-adjacent name, a flood of five-star reviews, and boilerplate descriptions that closely mirror genuine cryptocurrency storage tools.
However, beneath its carefully crafted exterior lay a purpose-built attack mechanism. Instead of relying on traditional web servers or external command-and-control infrastructure that might easily be flagged by antivirus engines or browser safety filters, the extension covertly captured user seed phrases and systematically emptied wallets by encoding stolen secrets directly into micro-transactions on the Sui blockchain.
The malicious software was uncovered, installed, and thoroughly analyzed by Socket, a security tooling company specializing in open-source software supply chains. Following the discovery, Socket published a comprehensive postmortem report detailing how the "Safery" extension successfully evaded detection, manipulated the Chrome Store search rankings, and exfiltrated sensitive seed phrases without triggering immediate security alarms. The findings serve as a stark warning to the broader digital asset community, highlighting that browser extensions remain a dangerously overlooked blind spot in cryptocurrency security architecture.
What distinguished this particular incident from more conventional crypto scams was the methodology employed by the threat actors. While the theft of seed phrases is an unfortunately frequent occurrence in the Web3 ecosystem, attackers typically rely on spoofing established wallet brands, cloning popular interfaces like MetaMask, or deploying recycled phishing domains. "Safery" took a distinctly different path. It forged an entirely novel identity, utilizing purchased or botted fake reviews to artificially boost its search ranking and launch as a brand-new, independent wallet option.
Because the extension did not impersonate a pre-existing trademark, the listing lacked the typical red flags that security-conscious users are trained to spot. There was no broken grammar, no suspicious permission requests, and no redirection to shady, unverified external domains. The official Chrome Web Store publisher page displayed zero prior consumer complaints, and its designated support URL led to an off-platform website that had not yet been flagged by security trackers at the time of Socket’s investigation.
Given its professional presentation, ordinary users browsing the store would have felt little hesitation before clicking the "Add to Chrome" button. The extension requested permission to run on "all websites"—a standard operational requirement for cryptocurrency wallets that must interact seamlessly with a wide array of decentralized applications. Notably, the software did not prompt users for extra, unusual permissions or attempt to inject complex content scripts that might have tripped Chrome’s more aggressive automated security warnings. Its branding remained minimalist, its companion website mirrored the extension’s exact name, and the initial setup interface directed users through standard wallet creation and import procedures.
The Seed Heist, Broadcast Over Sui
The true destructive phase of the operation initiated the moment a user inputted their seed phrase into the application interface. Rather than storing the recovery phrase locally or utilizing standard encryption methods for user access, the extension silently fragmented the sensitive text. It then encoded these individual pieces into what appeared to be entirely random wallet addresses.
According to Socket’s investigative research, these encoded fragments were directly injected into Sui blockchain transactions. The extension orchestrated minuscule SUI token transfers—amounts so negligible that they would instantly escape the notice of casual observers—directed toward addresses completely under the control of the attacker. Embedded quietly inside those micro-transactions, either concealed within memo fields or obfuscated directly within the transaction addresses, were the broken-down components of the victim’s seed phrase.
This tactical strategy provided significant operational advantages for the hackers. Because the payload left the compromised device disguised as an ordinary, legitimate blockchain transaction routed through a widely utilized, low-fee layer-1 network, the extension had no need to send outbound network requests to malicious servers. There was no telltale command-and-control beacon or data exfiltration routed over standard HTTP or WebSockets protocols that an active browser or third-party antivirus software might intercept and flag.
Once the data reached the public blockchain, it remained publicly accessible without requiring any further interaction with the victim’s machine. The attacker could retrieve the fragments at their leisure, reconstruct the complete seed phrase, and systematically sweep assets from the victims’ wallets across Ethereum or other supported layer-1 networks where the funds were actually held.
Effectively, the scammers repurposed the Sui blockchain itself as an encrypted, low-latency communications channel. Because the Sui network boasts exceptionally fast transaction confirmation times and negligible gas fees, it functioned perfectly as a covert message bus. Socket successfully traced multiple instances of these anomalous seed-fragment transactions, definitively establishing the causal link between the entry of the seed phrase within the malicious extension and the subsequent financial losses suffered by users.
Evidence gathered during the analysis suggests that the publisher likely tested this methodology in private development builds before deploying the version that ultimately captured prominent placement in the Chrome store search results. Earlier iterations apparently experimented with simpler, less refined data leakage techniques before perfecting the Sui encoding mechanism. By the time security analysts caught up with the active extension, it had already accumulated enough installations to secure a coveted spot on Chrome’s "trending" tier, which further amplified its visibility to unsuspecting users searching for storage solutions.
How the Chrome Algorithm Let It Happen
The rapid rise and success of the "Safery" wallet relied heavily on the underlying ranking logic of the Chrome Web Store. The store’s search algorithm determines placement by weighing several automated factors, including keyword matching, total installation counts, review velocity, average user ratings, and the recency of the last software update.
Extensions that experience a sudden, unnatural burst of activity—particularly within specialized or niche categories—can climb search results swiftly if established, better-vetted competitors fail to update their listings frequently. In this scenario, "Safery" combined a high-scoring keyword-optimized title with a sudden blitz of positive ratings, many of which were clearly templated or duplicated, alongside a contemporary upload timestamp.
Available evidence indicates that Google did not subject this specific listing to manual human review prior to publication. Policies governing the Chrome Web Store typically subject newly submitted extensions to a rapid automated scan combined with fundamental static analysis. Deeper, more rigorous scrutiny is generally reserved for extensions that request elevated permissions, such as direct access to browser tabs, system clipboards, local file systems, or browsing history. Because cryptocurrency wallet extensions frequently manage to bypass these specific warning flags by operating securely within localized iframes or utilizing standard, approved application programming interfaces, "Safery" stayed neatly within acceptable boundary lines.
Even when early users began voicing concerns and raising alarms across public forums, the time elapsed between initial reports and the eventual takedown by platform administrators stretched out long enough for substantial financial damage to occur. Part of this vulnerability is structural; the Chrome ecosystem does not automatically remove flagged extensions instantly unless there is an overwhelming consensus of reports or definitive, known malware signatures matched by automated tools. Because the malicious payload consisted of obfuscated JavaScript that leveraged decentralized blockchain infrastructure rather than external, centralized host servers, traditional malware detection signatures failed to identify the threat in real time.
This incident is far from the first instance of browser extensions being weaponized to target cryptocurrency assets. Past security breaches have involved deceptive applications such as fake Ledger Live desktop companions prompting users for recovery phrases, or compromised legitimate extensions where attackers managed to hijack the original developer’s publishing cryptographic keys.
However, the "Safery" case stands apart due to the seamless nature of its user-facing facade and the complete absence of traditional backend infrastructure. There was no rogue phishing website to shut down or command server to block; there was merely a self-contained browser extension quietly moving confidential secrets onto a public distributed ledger and vanishing into the background.
For users who fell victim to the exploit, recovery options were severely limited and relied heavily on rapid intervention. Security analysts advised affected individuals to uninstall the malicious software immediately, revoke outstanding token approvals, and rapidly sweep remaining digital assets to a newly generated wallet using an entirely clean, uncompromised device. For users who failed to notice the silent exfiltration in time, or those who kept substantial cryptocurrency balances directly within vulnerable hot wallets, asset recovery remained virtually impossible.
Security researchers and independent developers are now increasing pressure on platform operators to implement stronger heuristic defenses directly within the browser environment. Proposed remedies include automatically flagging any newly submitted extension that incorporates user interface elements prompting for standard 12- or 24-word recovery phrases. Additional recommendations include enforcing mandatory publisher identity attestations for wallet extensions, ensuring verifiable cryptographic proof that a listed publisher genuinely controls the underlying codebase for a recognized brand, and instituting much tighter regulatory inspection of wallet-related permissions.
The incident has reignited profound questions regarding the fundamental role of web browsers in decentralized finance. Browser-based wallets originally gained widespread adoption due to their unmatched accessibility and convenience, allowing users to interact smoothly with complex decentralized applications without needing to switch platforms or install standalone native desktop software.
Yet, that very accessibility has introduced significant risk exposure, turning the everyday browser into a high-risk environment susceptible to extension manipulation, session hijacking, clipboard scrapers, and covert on-chain exfiltration techniques. As the Web3 landscape continues to evolve, developers and security experts alike are forced to reconsider established distribution models, reminding users that in the realm of self-custody, convenience often carries hidden costs.