Federal Bureau of Investigation agents have arrested a high-ranking executive at a Canadian cybersecurity firm in connection with an escalating international investigation into the notorious ShinyHunters hacking collective. The arrest follows a high-profile cyberattack by the group that compromised sensitive internal records belonging to thousands of law enforcement personnel. Multiple sources familiar with the ongoing probe confirmed the details of the operation to KrebsOnSecurity.
The New York Times reported that federal authorities apprehended a Canadian national in Pennsylvania on suspicion of providing assistance to the ShinyHunters group. While neither the initial Times report nor a statement posted to social media by FBI Director Kash Patel identified the individual by name, sources close to the federal investigation revealed that the suspect was visiting Pennsylvania to attend a prominent cyber insurance and risk management conference. Investigators noted that the suspect’s professional background centered heavily on handling high-stakes ransomware negotiations and extortion advisories on behalf of corporate clients.
Further inquiry into the conference schedule indicates that the annual Cyber Risk Summit took place at the Loews Philadelphia Hotel. According to the event’s official documentation, one of the primary corporate sponsors for the gathering was a prominent Canadian security firm named Cypfer. Online professional profiles and corporate records subsequently linked the arrested individual to the wider sphere of Canadian cybersecurity and incident response firms, including past associations with Cypfer and another security entity that also sponsored the Philadelphia summit.
Following the initial apprehensions, federal court records in Pennsylvania confirmed that an individual named Edward Dobrovsky—with a slight spelling variance in the last name—was taken into custody on October 8 on charges of cyber extortion and conspiracy. While several core documents, including the primary criminal complaint, remain under seal, a subset of the docket was publicly indexed on legal research platforms. The available court summaries charge the defendant with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges related to the interference of commerce through threats.

U.S. Bureau of Prisons inmate records indicate that a 54-year-old individual matching the suspect’s description was initially held at a federal detention facility in Philadelphia. However, court filings show that the case was swiftly transferred to the U.S. District Court for the Eastern District of Texas. Sources indicate that the Texas field office has become the centralized command center for the overarching federal investigation into ShinyHunters. Representatives for the FBI declined to comment on the specifics of the arrest or the ongoing judicial proceedings.
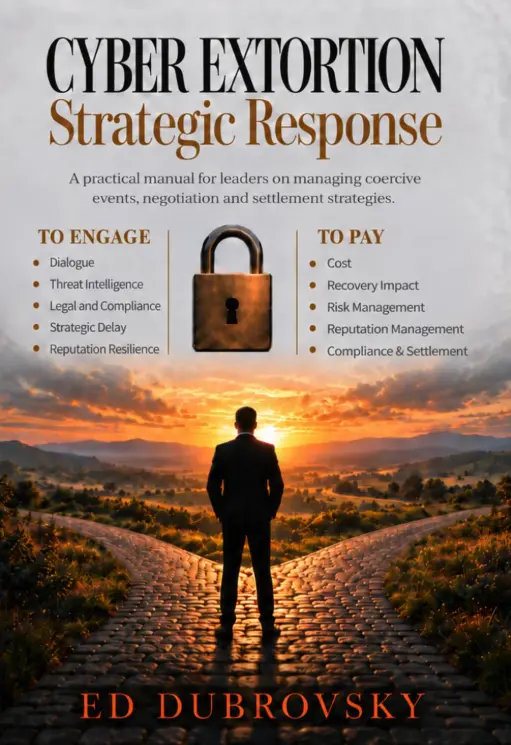
The suspect’s professional background includes authorship of a specialized book detailing the strategic responses required during cyber extortion events. The publication focuses heavily on the nuanced decisions corporate executives must make when faced with digital threats. Promotional material for the work emphasizes a core philosophical distinction frequently debated within the incident response community: that maintaining communication with cybercriminals is distinct from negotiating a payment, and that entering into discussions does not inherently constitute a commitment to meet extortion demands. Instead, industry experts often utilize engagement strategies to evaluate attacker claims, gather critical intelligence, buy time, and preserve tactical options while organizations assess their broader recovery posture.
Mr. Dubrovsky could not be immediately reached for public comment following his detention, and representatives for his associated firms did not immediately respond to inquiries. Court records available at the time of the arraignment indicated that he had not yet retained private legal counsel, nor had a public defender been formally appointed by the presiding court.
The ShinyHunters syndicate has established a reputation for deploying aggressive phishing tactics and leveraging stolen credentials to infiltrate corporate software-as-a-service accounts. Once inside corporate environments, the group siphons proprietary data and threatens public leaks unless substantial extortion fees are satisfied. According to federal estimates, the collective has successfully extracted more than $70 million from victims over the course of the year.
The current arrest is part of a broader, rapidly accelerating international crackdown on the cybercrime ecosystem. Sources familiar with the investigation report that federal agents have spent weeks analyzing digital devices seized during a raid orchestrated by Dutch law enforcement. That operation led to the apprehension of reformed hacker Pepijn van der Stap, whose arrest served as a significant breakthrough in the wider ShinyHunters case. Investigators have signaled that additional charges against principals and associates at various firms specializing in ransomware negotiation could be forthcoming as the probe widens.

The pressure on the hacking collective intensified dramatically following Van der Stap’s arrest. A prominent threat actor operating under the alias "Rey" assumed control of the ShinyHunters group and began brazenly taunting law enforcement agencies online. The group boasted about breaching an online recruitment portal utilized by the FBI, exposing personal details including departmental units, professional specializations, and confidential medical and psychiatric records of federal personnel.
International media outlets reported that the individual operating as Rey was identified as a teenager named Saif Al-din Khader. Authorities detained the young hacker, who subsequently began cooperating with federal investigators. The apprehension occurred as the cybercrime group attempted to execute an extortion campaign against a digital aviation and navigation unit that had been recently divested from Boeing.
As federal authorities continue to execute search warrants, analyze seized hardware, and coordinate cross-border enforcement actions, the investigation into the intersection of corporate cybersecurity intermediaries and cybercrime syndicates remains active and subject to rapid developments.