The development team behind Solidity has officially announced the release of Solidity v0.8.38, introducing critical bug fixes, performance optimizations, and preliminary warnings to prepare smart contract developers for the upcoming Amsterdam network upgrade. The new release addresses a low-severity bug discovered in the Yul optimizer, enhances the performance of underlying compiler infrastructure, and adds warning mechanisms for upcoming Ethereum Virtual Machine (EVM) opcode changes introduced via Ethereum Improvement Proposal (EIP) 8024.
As smart contract security and compilation efficiency remain top priorities for the Ethereum ecosystem, the release of version 0.8.38 marks another step forward in refining the Solidity compiler toolchain. Developers deploying applications across decentralized networks are encouraged to review the changelog and evaluate their compilation pipelines for optimal performance and safety.
Performance Boosts and Pipeline Optimizations in the Yul Optimizer
A major focus of the Solidity v0.8.38 release is improving compilation speed and efficiency through enhancements made to the DataFlowAnalyzer. Because several optimization steps within the Yul optimizer rely directly on the DataFlowAnalyzer, performance gains in this component ripple outward, resulting in faster compilation times whenever the Yul optimizer is enabled.
In addition to overarching performance improvements, developers utilizing the Intermediate Representation (IR) pipeline will benefit from a more streamlined function dispatcher. Specifically, the compiler now utilizes one fewer instruction to verify that incoming calldata is sufficiently long to hold a valid function selector. While minor at the instruction level, such optimizations contribute to more gas-efficient deployment patterns and optimized bytecode footprints across complex decentralized applications.
Preparing for EIP-8024 and the Amsterdam Network Upgrade
Looking ahead to future network configurations, Solidity v0.8.38 introduces early compiler warnings designed to safeguard developers against future breaking changes associated with the Amsterdam network upgrade. The compiler will now issue a warning whenever the identifiers swapn, dupn, or exchange are utilized as variable names or identifiers within Yul blocks or inline assembly.
These specific terms correspond to new opcodes introduced by EIP-8024 for the Amsterdam EVM version. Starting with that specific EVM version, these names will transition into officially reserved identifiers. Consequently, just like the pre-existing SWAP1 through SWAP16 and DUP1 through DUP16 opcodes, these newly introduced opcodes will remain unavailable for use as custom identifiers within Yul or inline assembly blocks. The development team has clarified that standard Solidity identifiers utilizing these names outside of inline assembly or Yul contexts are completely unaffected by the warning system, though proactive renaming is strongly advised to ensure a smooth transition for future upgrades.
Important Bug Fixes: Yul Optimizer Knowledge Base Stale Bookkeeping
The most critical component of the Solidity v0.8.38 release is a fix addressing a low-severity vulnerability cataloged as the Yul optimizer knowledge base stale bookkeeping bug, which affected compiler versions from v0.8.19 through v0.8.37.
To understand the mechanics of the bug, one must look at how the Yul optimizer operates. The optimizer actively tracks the contents of both memory and storage locations to intelligently replace load operations with known values and to strip away store operations deemed redundant because they do not alter existing state. However, a flaw could manifest when a Yul variable used specifically for computing memory or storage addresses underwent reassignment. Under these specific conditions, the optimizer occasionally failed to register that its internal knowledge base concerning those particular addresses had become stale.
As a direct consequence of this outdated bookkeeping, the compilation process could potentially replace a necessary memory or storage load with an outdated value, or incorrectly eliminate a store operation that was required for correct program execution. The scope of vulnerability depends heavily on the compilation pipeline used. Code compiled with the --via-ir flag could theoretically be affected across any context, whereas code compiled using the default evmasm pipeline was restricted primarily to compiler-generated Yul utility functions and isolated inline assembly blocks.
Despite the theoretical risk posed to a wide range of previous compiler versions, empirical investigation suggests that the actual occurrence rate of this bug in real-world scenarios is exceptionally rare. To measure the impact, the Solidity team compiled all verified smart contracts present within the Sourcify database using affected compiler versions both with and without the fix applied. Across the entire dataset, the resulting bytecode remained identical in every single instance. This exhaustive test strongly indicates that triggering the bug requires rare, highly specific conditions that rarely manifest in production smart contracts.
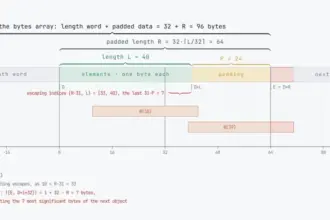
The discovery of the bug is credited to collaborative security research within the Ethereum community. Daniel Boye initially identified and reported the issue through the Ethereum Foundation’s bug bounty program. A subsequent, independent report submitted by Surya Prakash Akula further demonstrated that the vulnerability could theoretically be triggered directly from standard Solidity code without requiring the explicit use of inline assembly blocks. A comprehensive technical write-up detailing the vulnerability has been published by the core team for developers seeking deep architectural insight into the fix.
Full Changelog and System Updates
Alongside the critical security patch and upcoming upgrade preparations, the full changelog for version 0.8.38 encompasses various minor bug fixes, build system improvements, and updates to the solc-js JavaScript bindings, ensuring stability across diverse developer environments and automated continuous integration pipelines.
How to Install and Upgrade to Solidity v0.8.38
Developers and smart contract engineers wishing to upgrade their development environments to Solidity v0.8.38 should consult the official installation instructions available in the official Solidity documentation. The release packages and pre-compiled binaries are readily accessible via the project’s official GitHub repository.
For those compiling the Solidity compiler directly from source code, the development team explicitly advises against downloading the generic source code archives automatically generated by the GitHub interface. Instead, developers must use the official solidity_0.8.38.tar.gz source tarball provided in the release assets or check out the tagged v0.8.38 commit directly through Git to ensure proper dependency management and build integrity.
The core team concluded the release announcement by extending appreciation to all independent security researchers, community contributors, and developers whose ongoing feedback and auditing efforts continue to strengthen the security and resilience of the broader Solidity ecosystem.