The Solidity development team has officially announced the release of Solidity v0.8.37, marking another critical milestone in the evolution of Ethereum’s premier smart contract programming language. While primarily structured as a bugfix release, version 0.8.37 introduces three vital security-related bugfixes, addressing issues rated from low to medium severity, alongside crucial corrections for two smaller non-security miscompilations. Beyond patch management, the latest version expands experimental capabilities with a new stack shuffler for the SSA CFG code generator, incorporates support for the upcoming Amsterdam EVM version via the SLOTNUM opcode, and begins phasing out older features through targeted removals and deprecation warnings.
Crucial Bugfixes and Security Disclosures
The most pressing focus of Solidity v0.8.37 centers on resolving three distinct bugs discovered in previous compiler iterations. These fixes underline the ongoing commitment of the Ethereum Foundation and external security researchers to maintain the robustness of the Solidity compilation pipeline.
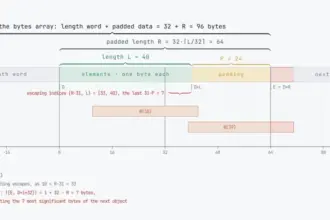
The first major vulnerability concerns memory byte array element deletion. When the delete operator was applied to an individual element of a bytes array stored in memory, the legacy evmasm compilation pipeline incorrectly wrote 32 zero bytes starting at the target element location instead of clearing only the single designated byte. Consequently, this erroneous behavior resulted in extra zero bytes overwriting up to 31 subsequent bytes. Depending on array positioning, these overwritten bytes could corrupt later elements within the same array or spill over into adjacent memory allocations following the array boundary. This issue similarly affected string values that had been converted into bytes.
Crucially, developers utilizing the IR (Intermediate Representation) pipeline remained unaffected by this bug, and equivalent assignments using direct element modification, such as b[i] = 0, properly cleared exactly one byte across both compilation pipelines. Solidity versions up to and including v0.8.36 were impacted by this flaw. The issue was responsibly identified and reported by developer shaheenfazim through the Ethereum Foundation’s bug bounty program, prompting a comprehensive technical write-up by the core team.
The second significant bug addressed in v0.8.37 involves spill slot collisions occurring across mutual recursion scenarios. To work around the Ethereum Virtual Machine’s strict stack depth limitations, the stack-to-memory mover within the IR pipeline relocates specific local variables to predetermined memory offsets known as spill slots. However, under specific call graph configurations involving mutual recursion, the compiler reserved too few slots. As a result, variables belonging to two separate functions could be assigned identical spill slots even when both variables remained live concurrently. This overlap led to one variable being silently overwritten by another during execution.
This bug bears a close technical relation to the unsound spill issue in mutual recursion previously patched in version v0.8.36. Versions 0.7.2 through 0.8.36 are vulnerable when compiled using the --via-ir flag. The discovery was brought to light by Ng Sze Hon via the Ethereum Foundation bug bounty program.
The third crucial bug involves misordered named parameters when utilizing custom errors inside require statements. Within the IR pipeline, arguments for custom errors constructed with named parameters and passed directly into a require condition—such as require(condition, MyError(b: 2, a: 1))—were inadvertently organized onto the stack following the order of the call site rather than their formal declaration order. During the subsequent ABI encoding phase, these arguments could be incorrectly matched against parameters, leading them to be misinterpreted as entirely different data types.
While the encoder still generated a structurally valid payload adhering to the error signature, the payload failed to reflect the actual values instantiated by the developer. Plain revert MyError(...) statements and other language constructs utilizing named parameters remain unaffected. Because this anomaly exclusively impacts the revert data of transactions that are already failing, it leaves contract state integrity completely unharmed. This bug was reported by Carl of Cantina Security through the Ethereum Foundation’s bug bounty program.
Additional Miscompilation Patches
In addition to the primary security fixes, Solidity v0.8.37 resolves two minor miscompilations that are not classified as direct security vulnerabilities.
The first minor fix targets uninitialized function pointers located within packed storage slots. Under the evmasm pipeline, reading an uninitialized internal function pointer from a packed storage slot produced an incorrect value whenever a subsequently stored variable within the same slot held a non-zero value. Consequently, performing an equality comparison between such an uninitialized pointer and a default-initialized local function pointer could evaluate to false, despite neither pointer ever receiving an explicit assignment.
This anomaly exclusively impacts the evmasm pipeline and does not interfere with actual function execution calls made through those pointers. The issue manifests only when comparing packed pointers prior to assignment. Because internal function pointer values depend heavily on exact bytecode structures and are unstable across contract updates, the compiler already warns against such comparisons and intends to prohibit them entirely in a future breaking release. Triggering this behavior requires a very specific usage pattern that can be caught through standard unit testing.
The second non-security miscompilation fix addresses constants read across both checked and unchecked mathematical contexts. In the IR pipeline, code responsible for calculating the value of a constant was historically generated only once per contract, utilizing either checked or unchecked arithmetic depending on whichever use site was generated first. Subsequent use sites reused this identical code block. For constants whose initializers overflowed their designated data types, reading the constant inside a checked context could incorrectly omit required overflow panic behaviors, whereas reading the same constant inside an unchecked block could trigger a spurious revert.
Because all operands involved in the affected reads are established at compile time, the miscompiled outcome remains entirely deterministic and immune to external transaction manipulation. Exploiting this issue would require intentionally relying on a constant designed to consistently fail at runtime or intended exclusively for unchecked environments, which does not reflect normal development practices. The most realistic failure mode stems from oversight in contracts lacking adequate test coverage, where constant evaluation triggers a Panic on initial execution or missing checks produce wrapped values.
Notable Compiler Features and Experimental Enhancements
Solidity v0.8.37 introduces several meaningful advancements to compiler architecture, notably within the experimental SSA CFG code generator. The experimental SSA CFG code generator precomputes precise stack layouts for every instruction point in a program, relying on a stack shuffler to emit the necessary SWAP, DUP, POP, and PUSH instructions to transition between layouts.
Previously, this shuffler operated greedily, executing localized steps sequentially until achieving the target layout. Version v0.8.37 replaces this greedy approach with a planning-based shuffler. The new mechanism constructs an explicit plan mapping current stack items to their target locations before executing the plan in a bottom-up fashion. If reachability limits prevent standard SWAP or DUP execution, the shuffler compresses the stack and restarts from a revised plan. Initial benchmarks indicate that this structured methodology is significantly more efficient than its predecessor while maintaining comparable bytecode output sizes. The SSA CFG code generator remains experimental and requires --experimental --via-ssa-cfg flags to activate.
Looking toward upcoming Ethereum network upgrades, v0.8.37 adds native support for the SLOTNUM opcode introduced in the Amsterdam EVM version via EIP-7843. This opcode retrieves the beacon chain slot number associated with the current block. Solidity exposes this functionality through block.slotnum as a uint64 data type, while Yul and inline assembly environments gain access via the built-in slotnum() function. The SMTChecker has also been updated to support this new property. These features require compiling with --evm-version amsterdam. Beginning with the Amsterdam version, slotnum also becomes a reserved identifier within Yul.
Removals, Deprecations, and Maintenance
As part of ongoing efforts to streamline the compiler codebase, v0.8.37 removes two experimental features introduced in version v0.8.35: the Language Server Protocol mode (--lsp) and the Generic Solidity prototype (pragma experimental solidity). The LSP mode was unmaintained and incomplete; future language server tooling will be developed as a standalone architecture rather than tightly integrated into the compiler binary. Similarly, the Generic Solidity prototype—an early exploration toward Core Solidity—proved insufficiently flexible, with development shifting to the standalone solcore prototype as a foundation for future implementations.
The legacy, experimental ABIEncoderV2 pragma now triggers a formal deprecation warning. Having remained redundant since the introduction of pragma abicoder v2 in version v0.7.4 and its adoption as the default in v0.8.0, the pragma is a leftover from earlier experimental phases. Because many older projects and legacy dependencies still reference it, the deprecation warning provides developers adequate opportunity to remove it before final removal.
Continuing deprecation schedules initiated in version v0.8.31, v0.8.37 introduces deprecation warnings for older EVM target versions—specifically constantinople, petersburg, istanbul, and berlin—as well as for the SMTChecker’s BMC verification engine.
How to Install and Upgrade
Developers seeking to upgrade to Solidity v0.8.37 can access complete instructions through the official documentation portal. Release binaries and source distributions are hosted directly on the project’s GitHub repository. When building from source, developers are advised to avoid automatically generated GitHub source archives and instead utilize the official solidity_0.8.37.tar.gz tarball or check out the designated v0.8.37 git tag to ensure build integrity.