Google announced today that it has successfully worked alongside a coalition of industry partners to dismantle a sprawling botnet consisting of more than 1.3 million Android TV set-top boxes. These devices are shipped directly from manufacturers pre-installed with malicious software designed to secretly rent out unsuspecting users’ internet connections to strangers while simultaneously conducting extensive advertising fraud. Security experts involved in the complex takedown operation note that this decisive action is likely to sever the botnet’s access to more than 10 million additional compromised systems. These secondary targets include a wide variety of Internet of Things (IoT) products, such as Android-based healthcare devices, karaoke machines, and digital signage systems operating on local networks worldwide.
A comprehensive report published by the Google Threat Intelligence Group (GTIG) revealed that Google has officially severed all business and technical ties with Videostrong Technology Co., a prominent TV box manufacturer based in China. According to conclusions reached by GTIG and other independent security researchers, Videostrong was directly responsible for embedding the malicious code that automatically enrolled more than 1.3 million set-top boxes into a devastating botnet dubbed “XCPE,” a moniker derived from one of the malware’s core code components.
The GTIG report details how the XCPE botnet automatically equips infected devices with software that makes their unique internet protocol addresses available for resale by multiple commercial "residential proxy" services. These proxy services allow third-party customers to rent residential internet addresses as a mechanism to anonymize their web traffic, bypass geographic restrictions, or spoof their true geographic locations. As security researchers have documented extensively over the past year, commercial residential proxy services have increasingly become a primary source of unwanted and often malicious web traffic. This traffic is frequently leveraged by threat actors to execute account takeover attacks, orchestrate large-scale advertising fraud, and execute mass content scraping operations for artificial intelligence projects.
"Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices," the GTIG report states. The document notes that Google took aggressive legal action to successfully seize and disable the various domains and command-and-control servers that Videostrong relied upon to operate the botnet and push additional malicious payloads to victim devices. "A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors."
While Android TV streaming boxes constituted the vast majority of the compromised systems, the GTIG report highlights that identical XCPE malware variants were discovered embedded within a diverse array of other Android-based IoT hardware. This includes telehealth devices, commercial karaoke machines, and professional digital signage displays deployed in public and corporate environments.
Google maintains strict requirements that all Android device manufacturers must pass comprehensive compatibility and security assessments before their products can legally access official services, ensuring that hardware entering the market does not harm consumers. However, investigators discovered that Videostrong managed to circumvent these safeguards by engineering its firmware to load malicious software immediately upon a user booting up the device for the first time. Google confirmed that it has since updated its verification and security measures to address and close this specific weakness.
The GTIG report explicitly calls out a number of prominent residential proxy providers whose software development kits (SDKs) were routinely downloaded by hardware infected through the XCPE botnet infrastructure. Among those named is AppSalt, widely known as Honeygain, which was originally developed by Vilnius, Lithuania-based Oxylabs. In October 2026, Oxylabs and Honeygain completed a structural reorganization, launching as independent platforms under a new umbrella entity named Source. This corporate restructuring followed a significant $130 million funding injection from private equity firm Warburg Pincus, a transaction that reportedly valued the broader business at approximately $3.6 billion.

Another major proxy provider linked directly to the botnet ecosystem is NetNut, a sprawling residential proxy enterprise operated by Alarum Technologies, a publicly traded Israeli company. In July 2026, the Federal Bureau of Investigation collaborated with private industry partners to seize hundreds of domains associated with NetNut. Lawmaking and law enforcement authorities stated at the time that the company was responsible for operating a separate, massive botnet called Popa, which similarly enslaved standard consumer TV boxes to function as involuntary residential proxy exit nodes. Other commercial proxy providers explicitly named in the Google Threat Intelligence Group report include EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
The successful disruption of the XCPE botnet was aided by extensive intelligence contributions from a variety of cybersecurity startups and industry partners, including Synthient, a specialized firm that actively tracks the operational infrastructure of proxy networks. In January 2026, Synthient published groundbreaking research detailing the rapid, aggressive spread of the Kimwolf botnet. At the time of its discovery, Kimwolf was hammering enterprise and residential networks worldwide with record-smashing distributed denial-of-service (DDoS) attacks. Synthient’s research documented how Kimwolf managed to infect millions of Android set-top boxes virtually overnight by exploiting widespread security vulnerabilities inherent in these commercial residential proxy networks to pivot and compromise other connected Android devices residing on the local networks of unsuspecting consumers.
Synthient’s detailed technical research prompted dozens of residential proxy providers to hurriedly patch vulnerabilities in their infrastructure. This collective remediation helped fragment the monolithic Kimwolf botnet into much smaller, isolated clusters, rendering its incessant and disruptive DDoS attacks far easier for network operators and internet service providers to manage and mitigate. The research also drew the focused attention of the Motion Picture Association, a major trade organization representing the interests of Hollywood film studios. The MPA partnered directly with Synthient to purchase, tear down, and analyze a wide variety of popular Android TV set-top boxes, including several models actively infected by Kimwolf and related IoT botnet strains.
In a comprehensive research report published today, Synthient examined a popular, pre-infected TV streaming device sold under the brand name MECOOL by Skyworth Technology, a publicly traded manufacturing firm based in China. Synthient concluded that MECOOL devices also bundled the malicious software distributed by Videostrong Technology Co., effectively installing AppSalt, Honeygain, and various other proxy software components without user awareness.
Synthient founder Ben Brundage explained in discussions with security journalists that Videostrong’s malicious distribution network was also utilized to spread software for the Grass proxy service. This builds upon previous investigations, including a November 2025 security report where researchers from Censys discovered that the popular Superbox TV streaming appliance similarly bundled Grass residential proxy software. At the time of that initial disclosure, representatives for Grass publicly denied any formal or intentional affiliation with the streaming box manufacturer.
That same November 2025 investigation highlighted that Superbox and similar branded Android TV set-top boxes primarily acquire their customer base through aggressive marketing campaigns involving social media influencers on platforms like TikTok. These influencers frequently praise the hardware for its unique ability to provide users with access to hundreds of unauthorized or pirated pay-TV streaming channels for a single, low, up-front fee.
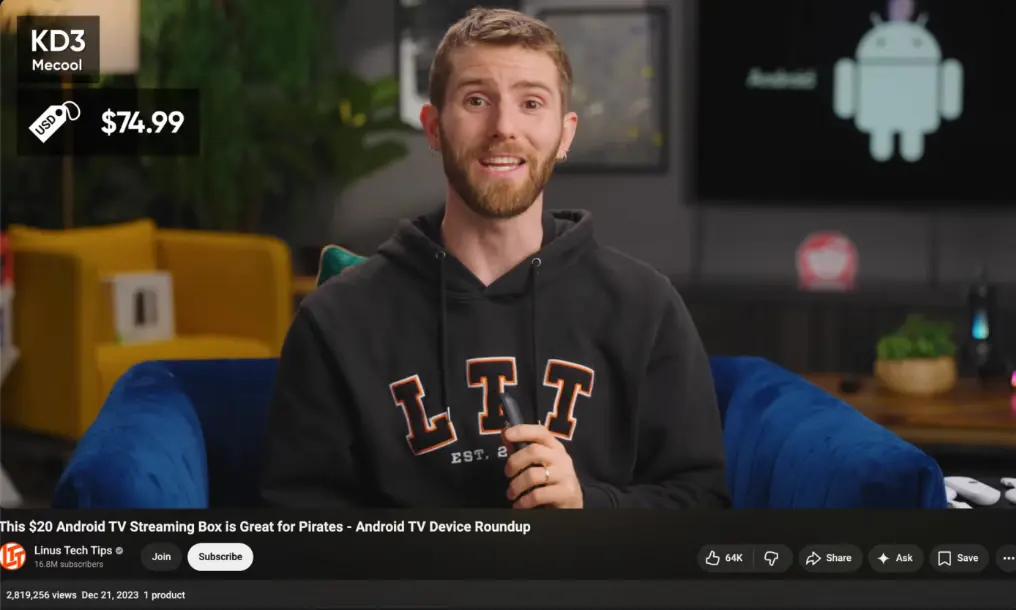
Similarly, Synthient’s newly released report observes that MECOOL set-top boxes experienced an explosion in commercial popularity after the hardware was featured in a 2023 video by the prominent YouTube channel Linus Tech Tips, which boasts an audience of nearly 17 million subscribers. In a formal statement shared with Synthient regarding the investigation, representatives for Linus Tech Tips confirmed that they have since updated the original video to explicitly frame the featured product as a consumer scam and have permanently removed all associated affiliate marketing links from the description.

While Google’s initial incident metrics focus heavily on the confirmed 1.3 million devices tied directly to the core XCPE botnet infrastructure, the GTIG report emphasizes that this figure only scratches the surface. The report estimates that the takedown will successfully sever access to at least 10 million additional compromised systems, noting that Videostrong’s various proxy and ad fraud affiliates maintained highly diversified distribution channels for their respective software modules well beyond the confines of the XCPE framework.
Synthient founder Ben Brundage echoed this assessment, characterizing the official 1.3 million device count as a highly conservative estimate of the threat’s true geographic and numerical scale.
"The scale of affected devices is likely way higher," Brundage said, describing the operation as perhaps the largest coordinated enforcement action against backdoored streaming TV boxes observed to date.
Providing additional context following the initial publication of these findings, Oxylabs issued a formal statement addressing the situation. The company explained that while its platform architecture is intentionally designed so that a residential device cannot be utilized as a proxy exit node unless the system receives a verifiable signal indicating that the end user has explicitly consented, rogue software developers and third-party suppliers actively fabricated and faked these consent signals.
"We have been conducting regular audits of the applications provided by our partners," Oxylabs said in its statement. "However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application."
The company’s statement added that while Oxylabs had no direct corporate records referencing an entity named Videostrong Technology Co., an internal review identified an external domain linked in the GTIG report as an active malware loader among its vendor list.
"As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry," the statement noted. "This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves."