The relentless threat of address poisoning scams continues to extract a heavy toll from the cryptocurrency community, preying on routine user habits and interface blind spots. In one of the most glaring examples of the vulnerability in recent weeks, a single crypto trader suffered a devastating loss of over $2.5 million worth of Tether (USDT) after falling victim to the exact same fraudulent scheme twice within a matter of hours.
The double incident highlights how sophisticated yet low-effort attack vectors can exploit even experienced participants in the digital asset ecosystem, capitalizing on the speed at which transactions are executed and the often-overlooked details within wallet transaction histories.
A Costly Double Mistake
According to reports published by blockchain security and analytics firm Scam Sniffer on May 26, the sequence of events began when the trader attempted to execute a standard transfer. Unbeknownst to them, the transaction history within their wallet interface had already been compromised by an attacker employing an address poisoning technique.
The first error occurred when the trader copied what they believed to be a legitimate recipient address directly from their recent transaction log. In reality, the address had been subtly manipulated to closely resemble the intended destination, featuring matching starting and ending characters. This minor visual oversight resulted in an initial transfer of $843,000 straight into the hands of the scammer.
Worse still, the trader failed to realize the breach before initiating subsequent transactions. Just hours after the initial loss, the victim repeated the exact same mistake. Operating under the assumption that the copied address in their history was safe or failing to double-check the full alphanumeric string, the trader sent an additional $1.7 million to the very same fraudulent address. By the time the realization set in, a cumulative total of more than $2.5 million in USDT had vanished into wallets controlled by malicious actors.
How Address Poisoning Works
The mechanics behind address poisoning—sometimes referred to as history poisoning—rely heavily on human psychology and user interface design rather than traditional software exploits or private key compromises.
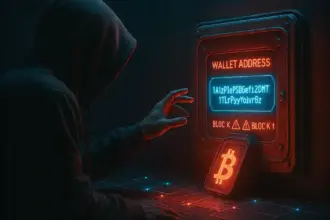
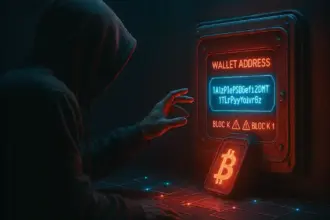
Attackers typically monitor public blockchain activity to identify frequent transaction pairs or active wallets. Once a target is identified, the scammers generate a "vanity address" or use automated tools to create a cryptocurrency address that shares identical prefixes and suffixes with an address the victim has previously interacted with.
The scammer then executes a dust attack, sending a negligible amount of cryptocurrency—or sometimes zero-value token transfers—from this lookalike address to the victim’s wallet. Because blockchains are public ledgers, this transaction appears directly in the user’s recent transaction history.
When the user later needs to send funds to a frequent contact, they often skip the tedious process of verifying every single character of the full address, opting instead to copy and paste the destination string directly from their recent transaction history. Because the malicious lookalike address sits near the top of the log, the user inadvertently selects it, transferring their capital directly to the attacker.

Security researchers note that these exploits are becoming increasingly common across various blockchain networks. Because they require minimal technical infrastructure compared to complex smart contract exploits or infrastructural hacks, attackers rely on the sheer probability that hurried traders will overlook the middle characters of a wallet address.
Broadening Threats: Social Engineering and Phishing
While address poisoning targets transaction habits, the broader threat landscape facing digital asset holders is expanding through increasingly aggressive social engineering campaigns. Blockchain security firm SlowMist recently highlighted a surging wave of SMS-based phishing operations designed to intercept and manipulate users under the guise of customer support.
In these sophisticated campaigns, malicious actors transmit deceptive text messages impersonating major centralized cryptocurrency exchanges, most notably Coinbase. The messages typically fabricate an urgent security crisis, warning the recipient of an unauthorized withdrawal, a compromised account, or an impending security breach that requires immediate intervention.
Victims are instructed to call a telephone number provided directly within the text message. Upon calling, the individual is connected to a fraudulent support agent posing as an exchange representative. Through psychological manipulation and a veneer of professional authority, the fake agent directs the panicked user to a meticulously crafted phishing website.
Once on the fraudulent portal, the user is prompted to input sensitive security credentials, including their wallet recovery phrase, mnemonic phrase, or private keys. Providing this information grants the hackers unrestricted, absolute access to the victim’s digital asset holdings, enabling them to drain funds across multiple chains instantaneously.
The financial impact of these social engineering tactics is staggering. Noted blockchain investigator ZachXBT has previously reported that similar support-impersonation and phishing schemes targeting Coinbase users alone have accounted for losses exceeding $300 million annually.
Industry Warnings and Defense Measures
As these attacks continue to evolve in frequency and scale, cybersecurity firms and blockchain analysts are urging market participants to exercise heightened vigilance when interacting with decentralized applications, wallet interfaces, and customer service channels.
SlowMist strongly advises crypto users to maintain strict security hygiene. This includes never sharing private keys or recovery phrases under any circumstances, entirely ignoring unsolicited communications, text messages, or phone calls regarding account security, and independently verifying any purported exchange issues by navigating directly to official websites or using verified mobile applications.
Furthermore, security experts recommend bookmarking frequently used wallet addresses rather than relying on recent transaction logs to avoid falling victim to address poisoning. Taking an extra moment to manually verify the entire string of a destination address before confirming a transfer remains one of the most effective defenses against multimillion-dollar human error in the digital asset space.