Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions carried out by the prolific and aggressive hacker collective known as ShinyHunters. The arrest, which took place in mid-September 2026, has sent immediate shockwaves through the underground cybercrime ecosystem. In the days immediately following the suspect’s detention, remaining members of the ShinyHunters group dramatically escalated their operations, launching high-profile retaliatory attacks that included stealing highly sensitive data from the FBI and extorting the notorious Russian ransomware group Cl0p.
According to three sources familiar with the matter, the Dutch man taken into custody by law enforcement this month is Pepijn van der Stap, a convicted cybercriminal residing in Almere and Lelystad in the Netherlands. Van der Stap was previously convicted in late 2023 for his involvement in a sweeping series of corporate data thefts and corporate extortions. Dutch prosecutors estimated at the time that those earlier cybercrimes generated illicit proceeds ranging between €1.5 million and €2.7 million.
During his high-profile trial in late 2023, van der Stap openly admitted to living a modern-day Dr. Jekyll and Mr. Hyde existence. Secretly operating under the hacker handle “Umbreon,” he used English-language cybercrime forums—including the now-defunct RaidForums and Breached—to extort corporate victims and auction off stolen databases. By day, however, van der Stap maintained a completely legitimate professional facade, working as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup. He also dedicated his free time to volunteering with the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit organization focused on security research and vulnerability mitigation.
Van der Stap fully confessed to his extensive data theft and extortion activities during court proceedings and was subsequently sentenced to four years in prison, with one year suspended. Bizarrely, during his trial, van der Stap opted to remain incarcerated in a secure facility rather than waiting out proceedings at home, arguing that he could not find comparable medical and psychological support on the outside for his ongoing mental health struggles, which he stated included post-traumatic stress disorder stemming from childhood trauma. He was ultimately released from custody in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, van der Stap portrayed himself as a completely reformed individual striving to turn his life around and make constructive contributions to society. At the time of the interview, he was employed as an offensive security lead at Neo Security, a Dutch cybersecurity firm that ultimately did not respond to media requests for comment regarding the arrest.
During that same conversation, van der Stap noted that he was still actively navigating lingering civil lawsuits and financial restitution obligations stemming from his past cybercrime activities, emphasizing that he was doing his best to make amends to his victims. However, shortly after that interview concluded, van der Stap abruptly stopped responding to communications. Attempts by close associates and colleagues to reach him repeatedly failed over a two-week span.
According to two sources with direct knowledge of the situation, van der Stap was arrested by Dutch law enforcement on or around September 16 and has since been held in custody for intensive questioning. One source confirmed that a colleague personally witnessed Dutch authorities carting physical items and electronic equipment out of van der Stap’s residence during the raid.
The arrest coincides with an intense ongoing manhunt by Dutch authorities, who had publicly appealed to the citizen for help in identifying a recorded voice in a telephone call from February 2026. In that audio clip, a native Dutch-speaking member of ShinyHunters successfully used sophisticated social engineering tactics to breach Odido, the largest mobile telecommunications provider in the Netherlands. During the intrusion, the hacker tricked an Odido employee into authenticating their credentials on a spoofed phishing website, giving the threat actors unauthorized access to data belonging to more than 6.2 million Dutch citizens.

Responding to inquiries from Dutch news media, ShinyHunters openly confirmed that the suspect heard in the police audio recording is indeed an active member of their decentralized collective.
"Our team member has our full support – emotionally, mentally, and financially," the hackers stated in a message shared with the NL Times. "Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them." At the time, it remained unclear whether Dutch police had definitively matched the Odido caller to a confirmed real-world identity, and the specific police unit handling the Odido investigation declined to comment.
The hacker collective also lashed out aggressively at Dutch law enforcement agencies. "The Dutch police will need all the luck in the world – and everyone’s prayers – if they want to catch him before we carry out another large-scale data theft in the Netherlands," the ShinyHunters statement read. "Frankly, the Dutch police are a big joke; they are incapable of doing anything. Incompetent. Irrelevant. Unimportant. Useless."
FBI and Cl0p Hacks
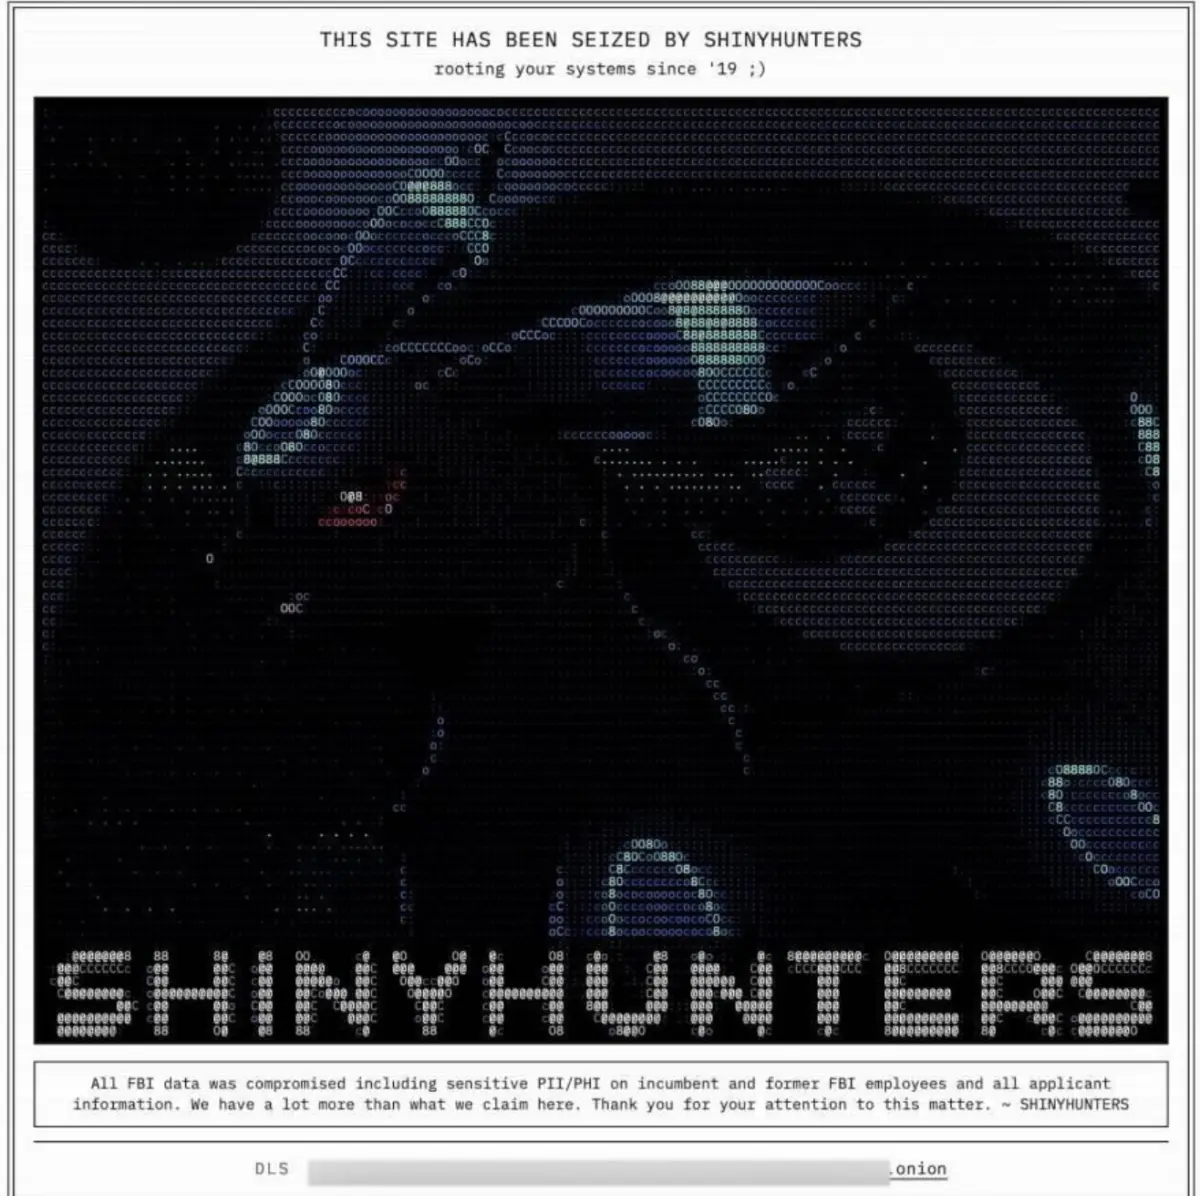
Just days after sources confirmed van der Stap’s detention by Dutch authorities, ShinyHunters claimed responsibility for an extraordinarily brazen cyberattack targeting the FBI’s job application portal, apply.fbijobs.gov. According to investigative reporting from 404 Media, the data compromised during the breach included Social Security numbers and highly sensitive personal identifiable information belonging to more than 5,000 bureau officials and applicants.
Both 404 Media and Reuters reported that the stolen FBI records detailed individual job titles and specialized organizational units, including special agents, threat intake examiners, members of the major cybercrimes units, and personnel tasked with investigating state-sponsored cyber threats from foreign adversaries. Furthermore, Reuters reviewed specific documents shared by the hackers which revealed that the cache included confidential psychiatric and medical files belonging to FBI personnel. The bureau subsequently issued a brief public statement confirming the compromise of the recruitment portal.
ShinyHunters asserted that they gained initial access to the FBI recruitment portal and numerous other corporate systems by exploiting a critical zero-day vulnerability, tracked as CVE-2026-35273, affecting PeopleSoft, an enterprise resource planning software-as-a-service platform developed by Oracle that is widely utilized by organizations for hiring, payroll, and human resources management. Oracle moved quickly to issue security updates for the PeopleSoft flaw after discovering that ShinyHunters had been weaponizing it as a zero-day since June. Concurrently, Mandiant released specialized web application firewall (WAF) rules designed to protect organizations unable to immediately deploy Oracle’s security patches.
However, security reporting from BleepingComputer revealed that ShinyHunters successfully bypassed Mandiant’s recommended mitigation rules by employing a clever URL-encoding trick. In a comprehensive threat intelligence report released on September 25, security experts at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that the collective had executed a mass-exploitation campaign targeting the PeopleSoft vulnerability, successfully exfiltrating data from dozens of enterprise systems spanning higher education, technology, healthcare, agriculture, transportation, and government sectors.
Significantly, van der Stap’s former hacker alias, Umbreon, appeared to be hidden in plain sight across the digital imagery distributed by ShinyHunters to publicize the FBI breach. The digital defacement banner left behind on the compromised FBI job portal featured an intricate ASCII art rendering of the Pokémon character Umbreon alongside a taunting message: "This site has been seized by ShinyHunters. rooting your systems since ’19 ;)." Security analysts noted that this graphic was virtually identical to the defacement assets utilized by ShinyHunters during their high-profile compromise of the English-language cybercrime forum Hackforums in 2020.

Multiple sources close to the unfolding law enforcement investigation into ShinyHunters indicated that the group’s recent high-risk attacks against both the FBI and Cl0p—one of Russia’s most established ransomware syndicates—represented a drastic departure from the group’s historically calculated operations. Observers noted this sudden tactical shift occurred following a leadership struggle within the collective, resulting in a takeover by a teenage cybercriminal from Amman, Jordan, known by the handle Rey. Rey operates as a core member of ScatteredLapsussHunters (SLSH), an umbrella cybercrime faction that security researchers describe as an amalgamation of three notorious hacking groups: Scattered Spider, LAPSUS$, and ShinyHunters.
According to insider sources, Rey harbored a persistent grudge against the Dutch hacker regarding control over the ShinyHunters brand assets and stolen data repositories. Consequently, cybersecurity analysts believe the prominent inclusion of the oversized Umbreon Pokémon imagery in the FBI recruitment site defacement was an intentional maneuver orchestrated by Rey to frame the imprisoned Dutchman.
Rey was first publicly unmasked by cyber intelligence firm KELA in March 2025. Ahead of a subsequent security profile published by KrebsOnSecurity in November 2025, reporters contacted Rey’s father to request an interview with his teenage son. Rather than blocking the inquiry, Rey’s father forwarded the message directly to the teenager, who subsequently admitted to participating in active ransomware operations while expressing a desire to distance himself from the SLSH collective.
Blaming Umbreon
Immediately following widespread media coverage of the FBI jobs site breach, Rey’s primary social media account on X (formerly Twitter), operated under the handle Ryan Moran (@rmoskovy), began aggressively taunting both the Cl0p ransomware syndicate and federal investigators. One posted meme crudely depicted the groups as the twin towers in New York City being struck by commercial airliners labeled “cl0p drama” and “fbi breach claim,” with a massive float-sized rendering of the Pokémon character Umbreon looming in the foreground.
On September 24, reporters again contacted Rey’s father to request interviews regarding his son’s apparent ascension to the leadership of ShinyHunters. Just hours after that outreach, Rey’s long-standing X account was abruptly deleted. Meanwhile, Rey’s father, an employee of Royal Jordanian Airlines, failed to respond to subsequent email inquiries concerning his son’s alleged illicit activities.
The underlying hostility between the SLSH faction and core members of ShinyHunters stems from a short-lived operational partnership earlier in the year. According to investigative reporting published by Wired, the two groups temporarily joined forces to monetize high-value corporate credentials accumulated by TeamPCP, an upstart cybercrime outfit that successfully compromised global code supply chains using malicious software but struggled to convert their stolen data into financial gains. (Two alleged leaders of TeamPCP were arrested in Australia, with one claiming in interviews that the group netted a mere $20,000 from their operations.)
Wired reported that Mandiant had covertly infiltrated TeamPCP’s infrastructure and was secretly responsible for burning the group’s stolen credentials by feeding them directly to major cloud infrastructure providers like Amazon and Microsoft, which promptly invalidated the keys. As the operation collapsed, the allied hacker factions began pointing fingers and blaming one another for rendering the stolen credentials worthless.
Wired reporter Andy Greenberg noted that shortly after partnering with TeamPCP, ShinyHunters went rogue, executing independent extortion schemes utilizing the compromised supply-chain credentials without distributing any profits to TeamPCP members. Mandiant researcher Austin Larsen estimated that ShinyHunters enjoyed a lucrative extortion streak throughout 2026, putting the collective on track to amass nearly $100 million in extortion payments over the course of the year.

Despite his extensive criminal history, van der Stap consistently maintained that financial gain was never his primary motivator. During interviews with Bloomberg reporters in 2024, he insisted his cyberattacks stemmed from an obsessive psychological compulsion to curate the world’s most comprehensive archive of stolen databases.
"The hacking was very easy for me, and it wasn’t a compulsion," van der Stap told Bloomberg. "My habit was collecting. Collecting data, organizing data, downloading data, creating folders."
Meanwhile, the DIVD, where van der Stap had previously volunteered, disclosed via social media that the organization had managed an internal cybersecurity incident involving the malicious use of artificial intelligence tools. While the nonprofit released limited details regarding the breach, a DIVD spokesperson confirmed to KrebsOnSecurity that the incident bore no connection to ShinyHunters and showed no indication of involvement by any former volunteers.
Dutch police subsequently confirmed the formal arrest of the 24-year-old suspect in connection with the ongoing ShinyHunters investigation. In a public statement issued via X, law enforcement officials announced that the man would appear before the chambers of the Rotterdam District Court, promising further transparency as the inquiry progresses.
Concurrently, Dutch media outlet RTL reported that investigators are examining suspicions that van der Stap attempted to orchestrate at least two murders overseas, with emerging indications suggesting the suspect may have issued explicit orders for the killings.
Adding international weight to the investigation, the FBI released a video statement delivered by Brett Leatherman, assistant director of the bureau’s cyber division. Leatherman thanked Dutch law enforcement partners for their crucial assistance and issued a direct warning to the remaining members of ShinyHunters to surrender voluntarily.
"Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left," Leatherman said. "The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours."