A teenager from Amman, Jordan, suspected of leading the prolific and aggressive data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the FBI to help identify other members of the hacking collective.
Security journalism outlet KrebsOnSecurity has learned that the young suspect—who operates online under the hacker handle "Rey"—was taken into custody just as ShinyHunters was actively engaged in the extortion of a business unit recently divested by global aerospace giant Boeing. In a striking twist of geopolitical and corporate overlap, this targeted Boeing subsidiary manufactures the fleet of aircraft utilized by the employer of Rey’s father: Royal Jordanian Airlines.
International Detainment and Online Personas
The initial breakthrough in the regional operation came to light when Reuters cited three unnamed sources confirming that a suspected ShinyHunters figure named Saif Al-din Khader had been detained in Amman by Jordanian authorities and was actively assisting the FBI. KrebsOnSecurity had previously identified Rey as Khader in a detailed cybersecurity profile published in November 2025, during which the young man openly acknowledged collaborating with multiple ransomware operations.
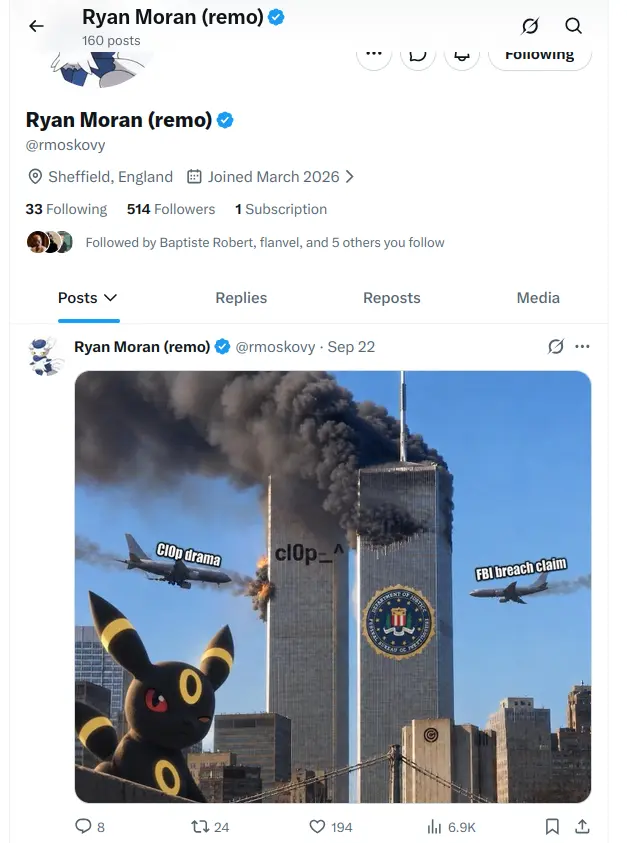
Rey’s digital footprint surfaced once again in late September during an exclusive report regarding the Dutch police’s arrest of 24-year-old convicted cybercriminal Pepijn van der Stap. Authorities suspected van der Stap of aiding ShinyHunters in their widespread data thefts and extortions. According to investigative findings, immediately following the Dutchman’s dramatic arrest on the evening of September 15, Rey seized operational control of the ShinyHunters brand. He wasted no time boasting publicly about executing a high-profile cyberattack to steal sensitive data from the FBI, while simultaneously claiming responsibility for extorting the notorious Cl0p ransomware group.
Using his long-standing account on Twitter/X, Rey taunted both federal law enforcement and the Cl0p syndicate with a series of memes. Cunningly, he embedded images of the avatar used by van der Stap’s former hacker alias, "Umbreon," in what investigators believe was a deliberate attempt to frame the arrested Dutchman for the fresh wave of attacks.
The operational backbone of these breaches relied on the mass exploitation of a critical software vulnerability (CVE-2026-35273) affecting Oracle PeopleSoft, a widely deployed software-as-a-service (SaaS) platform used across industries for human resources, payroll, and recruitment management. Oracle rapidly patched the vulnerability after ShinyHunters began weaponizing it as a zero-day exploit in June. Concurrently, cybersecurity firm Mandiant issued web application firewall (WAF) rules to protect organizations unable to immediately apply the security update.

Although initial attempts by the hackers to breach the FBI’s own PeopleSoft database in June were reportedly unsuccessful, the group later pivoted. By employing a classic URL-encoding trick, ShinyHunters successfully bypassed Mandiant’s suggested WAF rules, enabling them to strike dozens of systems across higher education, technology, healthcare, agriculture, transportation, and government sectors.
The consequences of these systemic breaches rippled outward. Reuters reported that the FBI removed an Accenture contractor over their failure to properly patch the federal recruitment portal targeted by the hackers. That breach exposed sensitive personal and professional details—including unit assignments, specializations, and medical records—belonging to more than 5,000 FBI personnel.
"Rey" Means King, as in Royal
According to two independent sources familiar with the ongoing multi-agency investigation into ShinyHunters, the digital aviation and navigation unit recently divested by Boeing was precisely the target of the group’s extortion attempts at the moment Rey was apprehended by Jordanian law enforcement. The FBI’s probe took on heightened urgency following this specific extortion attempt, largely because the stolen data allegedly posed severe operational safety and security risks.
In a brief statement provided to investigators and security researchers, Boeing acknowledged the attempted extortion by the threat actors. The company confirmed that the incident involved data linked to Jeppesen ForeFlight, a specialized subsidiary that Boeing sold to private equity firm Thoma Bravo for $10.55 billion in November 2025.
"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated. "We are actively reviewing the matter with the Jeppesen ForeFlight team."
A representative for Jeppesen ForeFlight maintained that their internal systems remained secure, noting in a written statement, "Based on our investigation to date into this claim and proactive security posture, there was no impact to our operations or products."

Rey’s alleged involvement in targeting the former Boeing asset carries added weight due to strong indications that his father is employed by Royal Jordanian Airlines. The airline is majority-controlled by the Jordanian government and operates its long-haul international routes using Boeing passenger aircraft. While Rey claimed on Telegram in early 2025 that his father worked as an airline pilot, that specific detail could not be independently verified.
However, forensic analysis of the family’s shared computer—which had previously been compromised by password-stealing malware—revealed that Rey’s father utilized identical credentials across multiple administrative and employee portals for Royal Jordanian Airlines. Neither Royal Jordanian Airlines nor the Khader family responded to requests for comment. Shortly after inquiries were sent to Rey’s father regarding his son’s activities, Rey began systematically scrubbing his social media accounts, including the Twitter/X profile used to taunt the FBI and Cl0p.
Despite purging most of his social media presence, Rey’s technical blog hosted on GitHub remained active. In March 2026, the blog featured an extensive investigative post that successfully doxxed two Russian men identified as the core developers and mastermind operators behind the Cl0p ransomware ecosystem.
Murder-for-Hire Allegations in the Netherlands
While the investigation into the young Jordanian hacker unfolded, Dutch media outlets published explosive allegations concerning Pepijn van der Stap, whose narrative of personal rehabilitation and transformation from cybercriminal to legitimate security professional had previously been celebrated within the tech community.
The Dutch daily newspaper RTL reported that investigators suspect van der Stap tried to orchestrate at least two murders. According to the reports, the violent acts were intended to be carried out abroad, and evidence suggested van der Stap issued the direct orders for the plots.
Van der Stap had recently completed the majority of a four-year prison sentence handed down for historic data theft and extortion activities that prosecutors estimated yielded between 1.5 million and 2.7 million euros. Following his release, he secured a position as an "offensive security lead" at Amsterdam-based cybersecurity firm Neo Security, telling security researchers his role involved auditing client networks for vulnerabilities.

Neo Security owner Benjamin Korper told reporters that the firm retained an outside forensic investigator to determine whether van der Stap had compromised Neo Security or any of its clients. Investigators reportedly found no evidence of malicious internal activity directed against the company. Korper confirmed that Dutch forensic police visited his office on the night of September 15, executing a high-profile raid that reportedly involved the deployment of flashbang grenades.
Before his initial arrest in 2023, van der Stap worked as a software engineer for Amsterdam cybersecurity startup Hadrian while concurrently volunteering for the Dutch Institute for Vulnerability Disclosure (DIVD), even as he orchestrated cyberattacks against prominent corporate entities.
When questioned about how the public or victims could trust a self-proclaimed reformed criminal who had deceived colleagues and investigators for years, van der Stap maintained that his actions and remediation efforts defined his current path. "You can throw a bunch of nice words at someone, but you can’t convince them if they don’t want to be convinced," he said. "I’m doing what I can to repay victims, and that’s all I can do."
Franchising and Burning a Brand
Security analysts point out that the individuals currently operating under the ShinyHunters banner are distinct from the original core members, most of whom are French nationals previously apprehended and prosecuted for similar cybercrimes. Over the years, ShinyHunters evolved less like a traditional tight-knit gang and more like a criminal franchise.
Security experts liken the group’s operational model to the fictional "Dread Pirate Roberts" from The Princess Bride, where leadership succession happens not through peaceful transition, but via arrests and law enforcement takedowns, often resulting in multiple actors claiming the mantle simultaneously. Investigators note that federal authorities are increasingly focusing on freelance affiliates who harvest and trade credentials to SaaS platforms in exchange for a percentage of subsequent extortion payouts.
In the wake of van der Stap’s arrest, underground Telegram channels associated with Rey erupted with criticism. Participants mocked the teenager after he backed down from public threats against law enforcement and the Cl0p cartel, and again when the ShinyHunters darknet portal abruptly went offline. Critics accused Rey of co-opting the dormant ShinyHunters brand for personal profit.

"He bought the old forum PGP key and used it to make new Breachforum websites and Telegram channels larping as ShinyHunters to ransom companies and then sell the used data or resell his forum when he goes broke," one community member alleged in a chat group.
A rival Telegram channel named "The Battle" dedicated significant attention to doxxing and ridiculing Rey and his associates. Administrators of the channel claimed that Rey caused significant financial and reputational damage while acting as an inexperienced opportunist riding the coattails of a notorious brand.
"Rey (Saif Al-Din Khader) made a serious mistake when he started pretending to be a member of ShinyHunters," the administrators wrote on Telegram. "That group had already been dismantled… yet Rey still chose to use its name while carrying out his crimes."
The group’s public posturing had previously prompted a direct response from law enforcement. In May 2026, the FBI issued a formal flash notice warning organizations against paying ransoms to ShinyHunters. The advisory detailed the syndicate’s aggressive harassment tactics, which included sending threatening messages, placing phone calls to victims and their families, and occasionally executing swatting attacks.
In interviews with tech media outlets, representatives of the hacker collective claimed their assault on federal infrastructure was designed to counter the FBI’s public advisories. However, industry researchers noted that the relentless pressure from law enforcement, combined with the steady unmasking of its rotating cast of operators, has severely damaged the group’s viability and commercial prospects for ongoing extortion schemes.