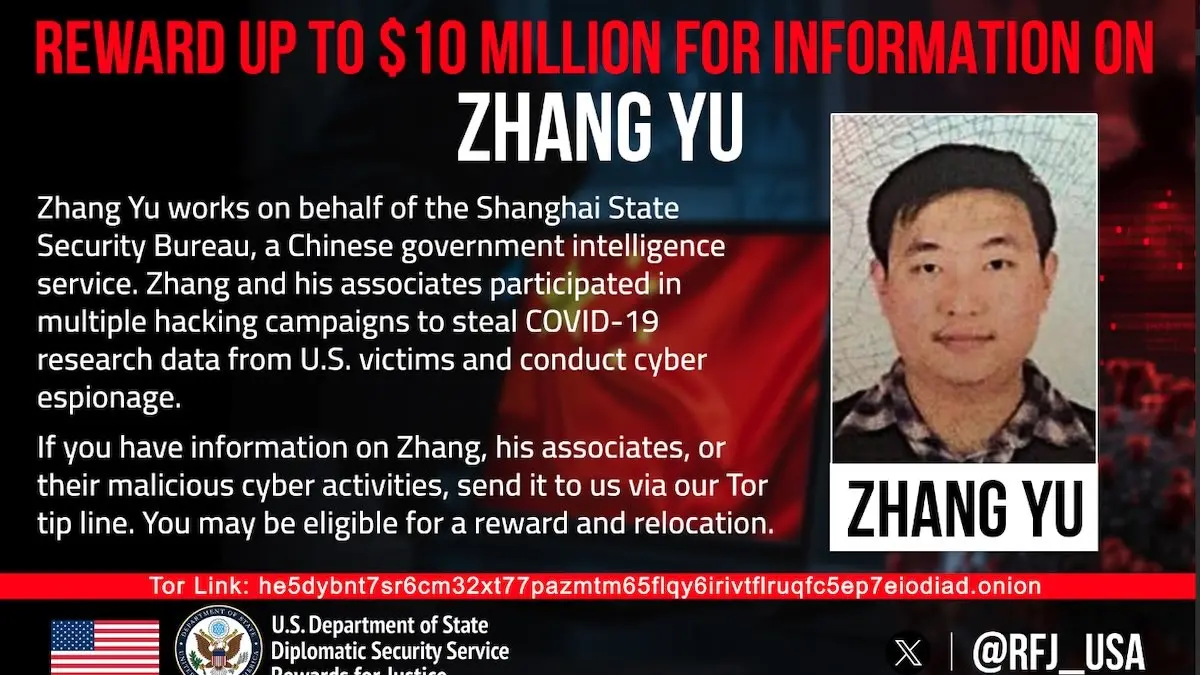
The United States Department of State has announced a substantial financial reward of up to $10 million for information leading to the location or identification of Zhang Yu, a Chinese national accused of playing a central role in the notorious Hafnium cyber-espionage campaign. The initiative, spearheaded by the State Department’s prominent Rewards for Justice (RFJ) program, underscores ongoing international efforts to hold state-sponsored malicious actors accountable for large-scale cyber operations targeting critical infrastructure, sensitive research, and commercial organizations across the globe.
According to the official announcement released by the Rewards for Justice program, Zhang Yu is a director at Shanghai Firetech Information Science and Technology Company. US law enforcement and intelligence assessments allege that Zhang operated on behalf of the Shanghai State Security Bureau (SSSB), which functions as a regional branch of China’s broader Ministry of State Security (MSS). The charges against Zhang place him at the heart of state-backed cyber operations that have repeatedly strained geopolitical relations and highlighted the persistent threat posed by advanced persistent threat (APT) groups operating within national borders.
Zhang is not facing these allegations alone. He was officially named alongside Xu Zewei in a comprehensive nine-count indictment that was unsealed by federal prosecutors in July 2025. The unsealing of the indictment followed a high-profile international law enforcement operation in April 2026, during which Italian police successfully arrested Xu in Milan at the explicit request of United States authorities. Following his arrest, Xu was extradited from Italy to the United States to face federal charges. He has since made initial appearances in a federal court located in Houston, Texas, where the judicial proceedings are moving forward. Meanwhile, Zhang Yu remains at large, prompting the State Department to issue the multi-million dollar bounty to incentivize global informants to come forward with actionable intelligence regarding his whereabouts.
The indictment outlines a systematic campaign of cyber intrusion and intellectual property theft spanning multiple years. According to the Rewards for Justice program and federal court documents, the malicious activities began in early 2020. During this initial phase, Zhang and his co-defendant Xu Zewei—who at the time served as a general manager at Shanghai Powerock Network Co. Ltd.—gained unauthorized access to proprietary research networks. Specifically, the hackers targeted COVID-19 research conducted by prominent United States-based universities, as well as leading immunologists and virologists, with the clear intent of siphoning off sensitive, high-value medical and scientific information during a global public health crisis.
As the scope and sophistication of the operations evolved, the duo’s targets expanded significantly. The following year, Zhang and Xu allegedly played key roles in exploiting critical vulnerabilities in Microsoft Exchange Server software as part of the broader Hafnium cyber campaign. The RFJ statement notes that this aggressive campaign successfully compromised tens of thousands of computers and enterprise networks worldwide. Among the domestic victims identified in the operation were a major United States university and a prominent US law firm, illustrating the indiscriminate nature of the data harvesting and network infiltration techniques employed by the threat actors.

The Microsoft Exchange server vulnerabilities exploited during the Hafnium campaign first came to widespread public and industry attention in March 2021, when Microsoft officially disclosed a series of zero-day flaws being actively leveraged in the wild. In the wake of these disclosures, the technology giant and the broader cybersecurity community began tracking the threat actor under the designation Silk Typhoon. When Xu Zewei was successfully extradited to the United States, the Federal Bureau of Investigation (FBI) revealed the staggering scale of the operation, noting that the Hafnium campaign had successfully compromised more than 12,700 organizations across the United States alone, causing widespread disruption, emergency patching efforts, and severe remediation costs for affected entities.
The newly announced $10 million reward for Zhang Yu falls directly under a specialized Rewards for Justice authority. This specific program tier offers financial incentives for credible information concerning any individual who targets United States critical infrastructure or engages in malicious cyber activities in violation of the Computer Fraud and Abuse Act, particularly when those individuals are acting under the direction, control, or orchestration of a foreign government. By leveraging financial rewards, the United States government aims to pierce the veil of state protection often afforded to international cybercriminals and encourage insiders or knowledgeable parties to share critical details that could aid in bringing fugitives to justice.