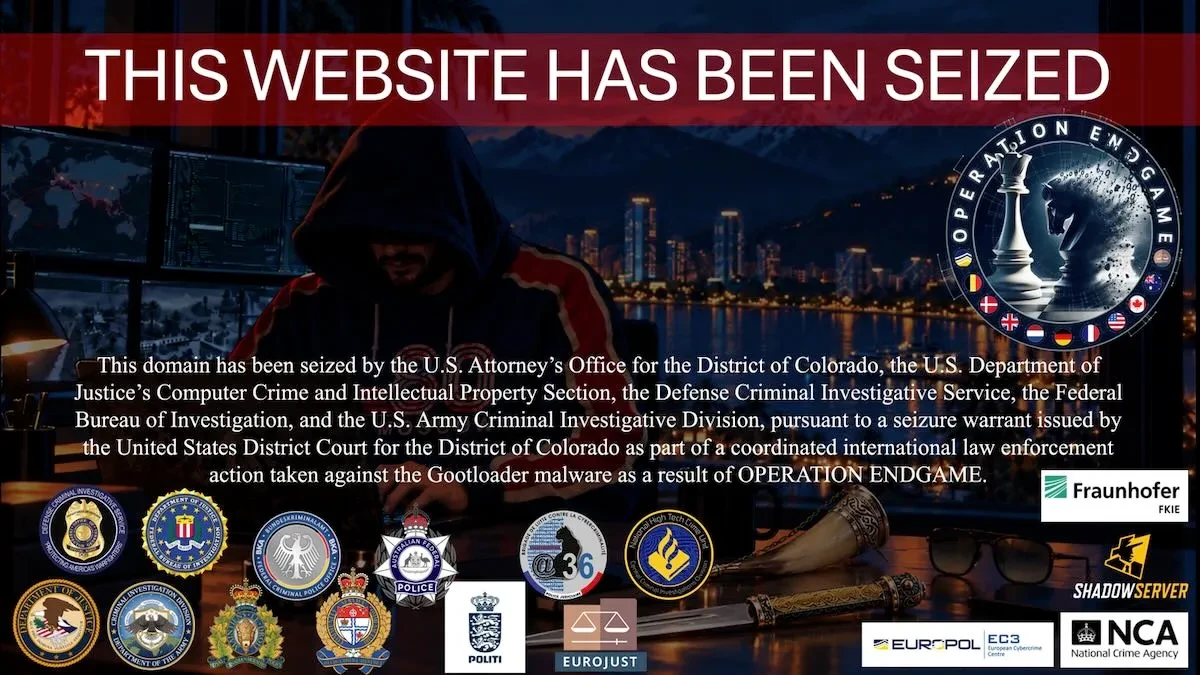
In a sweeping international crackdown on the cybercrime-as-a-service ecosystem, a coalition of law enforcement agencies from the United States, Europe, Australia, and Canada has successfully dismantled the core infrastructure behind three of the most notorious malware families currently plaguing the digital landscape: Gootloader, CastleRAT, and StealC. The coordinated effort, which represents a significant blow to the operational capabilities of sophisticated cybercriminal syndicates, resulted in the seizure of 235 servers and 257 domains, effectively severing the lifelines of networks that have facilitated ransomware attacks, large-scale data theft, and financial fraud for years.
The operation, which Europol described as a major tactical victory, was designed to neutralize the distribution mechanisms that allow these malicious tools to proliferate. By targeting the backend infrastructure—the command-and-control servers and the domains used to host malicious payloads—investigators have created a substantial barrier for the operators of these platforms. This disruption is the latest chapter in the ongoing international initiative known as "Operation Endgame," a strategic campaign aimed at identifying and dismantling the technical underpinnings of the modern cybercrime economy.
The Gootloader Menace: A Legacy of Deception
Among the targets of this operation, Gootloader stands out as a particularly long-standing and destructive threat. Active since at least 2018, Gootloader has functioned primarily as a highly effective "dropper," a type of malware designed to gain an initial foothold on a victim’s machine before facilitating the installation of secondary, more malicious software, such as file-encrypting ransomware.
The modus operandi of Gootloader has historically relied on social engineering and web compromise. The attackers would inject malicious code into legitimate websites, often masquerading as providers of fake legal documents or corporate templates. When unsuspecting users visited these compromised sites, they were often prompted to download files that, while appearing benign, initiated the Gootloader infection chain.
According to the United States Department of Justice, the impact of Gootloader has been profound. Over its six-year history, the malware has been responsible for infecting more than 25,000 computers, leading to an estimated $28.8 million in damages within the U.S. alone. The recent intervention has forced the removal of the dropper from at least 100 servers, while Europol reported the seizure of 14 additional servers and 218 domains specifically associated with the network. Furthermore, in a massive effort to clean the digital environment, 681 websites that had been compromised by the group were sanitized, preventing further potential infections of legitimate users.
CastleRAT and the Escalation of Remote Access Threats
While Gootloader focuses on the initial breach, other tools like CastleRAT represent the more intrusive stages of a cyberattack. CastleRAT, a remote access trojan (RAT) that emerged around 2025, has been instrumental in providing threat actors with persistent, high-level control over compromised systems. By gaining administrative-level access to infected machines, the operators of CastleRAT have been able to exfiltrate sensitive data, monitor user activity, and ultimately deploy ransomware to extort victims.
The disruption of CastleRAT infrastructure was particularly surgical, with law enforcement seizing 120 servers and 39 domains. Perhaps most significantly, the operation resulted in the recovery of vast amounts of victim data that had been stored on these seized servers. Data shared with the security community, including the prominent breach-notification service HaveIBeenPwned, reveals the scale of the compromise: approximately 180,000 unique email addresses and 893,000 unique passwords were recovered. This cache represents a treasure trove of credentials that, had they remained in the hands of criminals, would have undoubtedly fueled further waves of unauthorized access and identity theft across global organizations.
StealC: Dismantling the Data-Harvesting Pipeline
The final pillar of this coordinated takedown targeted StealC, a specialized stealer and dropper that has been active since at least 2023. Unlike some malware families that focus exclusively on encryption or remote control, StealC is purpose-built for the systematic harvesting of credentials, personal identification, and sensitive browser data. It acts as a primary entry point for information theft, which is then sold on underground forums or used to facilitate deeper intrusions into corporate networks.
This recent action against StealC is a continuation of a broader campaign against the platform that began earlier this year, involving collaborative efforts between private sector giants like Microsoft and various international law enforcement agencies. By seizing 102 StealC servers, authorities have further eroded the infrastructure that supported the malware’s operations.
The global impact of these combined seizures is best measured in the sheer volume of stolen data recovered. Europol reports that the international operation secured 6.4 million victim datasets. These credentials have been distributed to a network of cybersecurity organizations and national computer emergency response teams, including the Dutch Institute for Vulnerability Disclosure (DIVD), CheckjeHack, NoMoreLeaks, Sekoia, The Shadowserver Foundation, and the Dutch National Cyber Security Centre (NL-NCSC). By placing this information into the hands of these defensive organizations, the authorities are ensuring that the victims can be alerted and that the stolen credentials can be rendered useless for future attacks.
The Cybercrime-as-a-Service Model Under Pressure
The success of this operation highlights the inherent vulnerabilities within the "cybercrime-as-a-service" business model. By commodifying the tools of cybercrime—offering droppers, stealers, and RATs as off-the-shelf products for other criminals to rent or purchase—these syndicates have achieved scale and efficiency that would have been impossible for individual hackers to replicate. However, this model also creates a centralized dependency on specific infrastructure. When law enforcement successfully strikes at these central hubs, the impact ripples through the entire criminal ecosystem, disrupting the services for thousands of downstream operators who rely on these tools to conduct their own attacks.
Europol emphasized that the primary motivation for these criminal groups is financial gain, often achieved by selling stolen credentials to other malicious actors who specialize in large-scale ransomware campaigns. By breaking this chain, the international coalition has not only stopped current ongoing attacks but has also made it significantly harder for these groups to monetize their future operations.
This coordinated effort serves as a reminder that while the threat of sophisticated malware remains constant, the collaborative power of international law enforcement, supported by private sector threat intelligence, remains the most effective tool in mitigating these risks. As the digital landscape continues to evolve, the ability of these agencies to synchronize their efforts across borders—as demonstrated by Operation Endgame—remains the best hope for securing the internet against persistent and adaptable criminal entities. The cleanup of these networks is a significant achievement, though it remains only one part of a larger, ongoing effort to secure the global digital infrastructure from those who seek to exploit it for profit and destruction.