Security analysts at BitMEX Research have issued an urgent warning to the cryptocurrency community regarding a sophisticated new scam targeting early Bitcoin holders, specifically focusing on dormant wallets dating back to the foundational years of the asset, such as 2011.
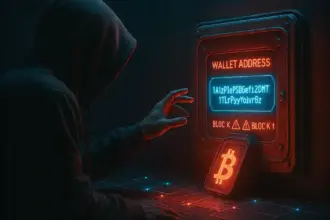
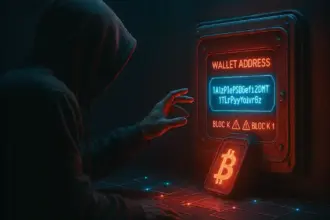
According to the research firm’s findings, the fraudulent campaign relies on exploiting long-inactive blockchain addresses. Perpetrators are injecting false transactions and misleading text messages directly into the blockchain data using OP_Return outputs. This optional field within a Bitcoin transaction allows users to carry arbitrary data on-chain, a feature that scammers are increasingly weaponizing to broadcast malicious payloads directly to unsuspecting holders or blockchain observers.
In one prominent and well-documented case uncovered by analysts, the attackers targeted the famous "1Feex" wallet. This specific address holds approximately 80,000 Bitcoin, a massive fortune that is widely believed to have been stolen during the historical hack of the Mt. Gox cryptocurrency exchange years ago. The attackers crafted a specialized message within this transaction stream designed to redirect anyone monitoring or claiming ownership of the address to a fraudulent website. This malicious portal has been meticulously designed to impersonate Salomon Brothers, a well-known, albeit defunct, Wall Street financial institution.
Fake Legal Claims and Coercive Tactics
Upon visiting the fraudulent website, targets are met with an official-looking legal notice that falsely declares the targeted wallet to be "lost or abandoned." The platform then attempts to coerce supposed owners into taking action to protect their multi-million-dollar assets. It invites individuals to prove their rightful claim by signing an on-chain message utilizing their private cryptographic key or by submitting sensitive personal and financial documentation through a web-based contact form. To create a strong sense of urgency, the fake legal notice dictates a strict deadline, warning that if no response is received by October 5, the wallet will be officially deemed legally abandoned under fictitious statutory rules.
BitMEX Research conducted a thorough review of the website and quickly established that the platform bears no credible affiliation whatsoever with the real Salomon Brothers or its historical leadership structure. While the fraudulent site attempts to build a facade of authenticity by displaying a list of real individuals who genuinely worked at the Wall Street firm during the 1980s, none of these former professionals have any connection to this newly emerged and spurious entity.
Industry analysts have noted that the operational approach closely mirrors an older, controversial scam associated with high-profile figures such as Calvin Ayre, who previously funded legal maneuvers involving the exact same Bitcoin address. BitMEX Research detailed these findings, pointing out the deceptive use of historical personnel to lend credibility to an entirely fraudulent operation.

"The links between this company and this website are fake," BitMEX Research stated in their public advisory. "There is a page with an ‘advisory board’ that contains real people who worked at Salomon Brothers in the 1980s, however, these people seem to have no link to this new spurious entity."
Community Reactions and Social Engineering Risks
As news of the campaign spread across public forums and social media networks, cryptocurrency community members quickly weighed in to analyze the mechanics of the attack. Security-conscious observers pointed out glaring operational security flaws in the scammers’ narrative. For instance, legitimate owners seeking to prove activity on a dormant wallet would logically need only to move a negligible amount of Bitcoin to a fresh address to demonstrate control, rather than transferring their entire multi-million-dollar balance or submitting sensitive personal identification documents to an unverified third party.
This glaring discrepancy has led many prominent security researchers and community analysts to conclude that the entire campaign is not actually about recovering lost funds, but rather functions as a targeted social engineering effort. The ultimate objective appears to be gathering sensitive personal information, private keys, or credentials under the guise of a formal legal proceeding.
In light of these findings, BitMEX has strongly emphasized that users, asset recovery specialists, and blockchain observers should avoid interacting with the fraudulent contact form, refrain from connecting wallets to the malicious site, and under no circumstances provide personal details or cryptographic signatures.
The emergence of this intricate scam highlights the constantly evolving and increasingly sophisticated nature of cryptocurrency fraud. The digital asset ecosystem continues to grapple with advanced threat actors employing psychological manipulation alongside technical exploits. According to broader industry data tracking digital asset crime, the first half of the year has seen bad actors successfully steal over $2.1 billion across 75 separate security incidents, representing a concerning 10% increase in stolen funds compared to the same tracking period from the previous year. As the total valuation of early crypto holdings continues to appreciate, dormant wallets are expected to remain prime targets for malicious actors seeking to exploit historical vulnerabilities.