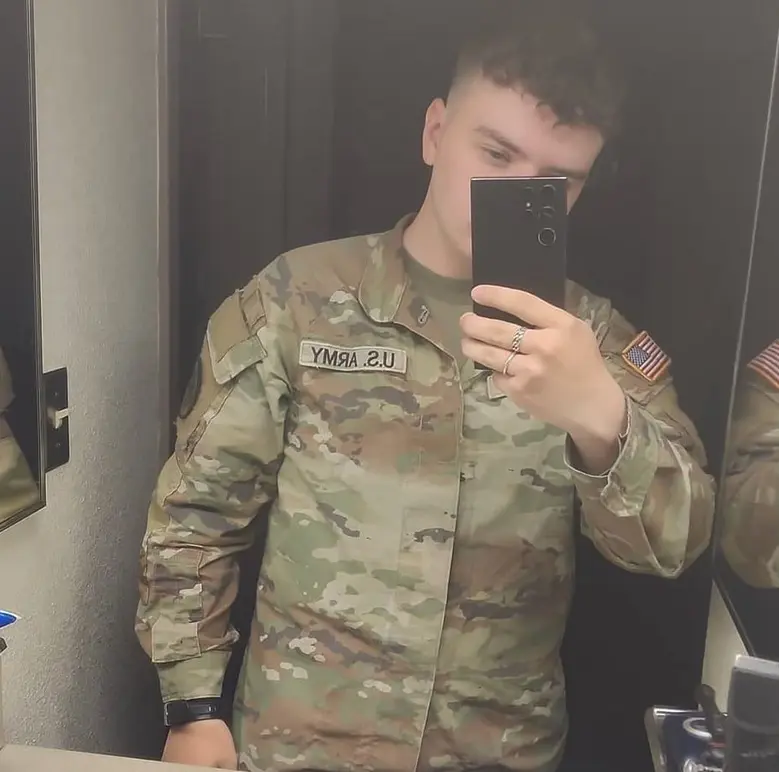
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced in a federal courtroom to 70 months in federal prison. In addition to the prison term, the judge ordered the former soldier to pay nearly $300,000 in restitution to his victims, bringing a significant chapter of a high-profile international cybercrime investigation to a close.
Cameron John Wagenius, a 22-year-old active-duty service member stationed at a U.S. Army base in South Korea at the time of his offenses, operated under the online cybercriminal moniker “Kiberphant0m.” Operating alongside a network of alleged co-conspirators, Wagenius exploited vulnerable cloud data storage services. Specifically, the group targeted large customers of the cloud data storage service Snowflake by leveraging exposed credentials and exploiting accounts that failed to enforce multi-factor authentication. In response to these widespread campaigns, Snowflake has since mandated multi-factor authentication across all accounts to prevent similar unauthorized access.
The scope of the illicit operations became apparent in October 2024, when Wagenius took to various cybercrime forums to boast about his digital exploits. He claimed to have successfully stolen the call and text metadata—including source and destination phone numbers, exact timestamps, and call durations—for tens of millions of AT&T customers. Furthermore, Kiberphant0m boasted about breaching more than a dozen major telecommunications companies globally, which included Verizon’s Push-to-Talk business. The cybercriminal group actively and publicly extorted these corporate entities, demanding payoffs in exchange for promises that the sensitive stolen data would remain unpublished.
Federal investigators quickly caught onto the digital footprint left by the threat actor. In late November 2024, security researcher Brian Krebs published warnings indicating that the individual operating as Kiberphant0m was likely a U.S. soldier stationed in South Korea. Less than a month after those public warnings surfaced, Wagenius was formally arrested. He was subsequently charged in two separate federal indictments and moved quickly through the judicial process, pleading guilty to all counts across both cases. During his sentencing hearing in Seattle, federal judges handed down the nearly six-year prison sentence alongside an order to pay $294,978 in restitution to cover the financial fallout of his crimes.
Prosecutors revealed during the legal proceedings that Wagenius did not operate in a vacuum. He was allegedly assisted in his extortion campaigns by Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, who possesses a well-documented and extensive history within the cybercriminal underworld. Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, a vast and dangerous collection of compromised Internet-of-Things devices that had been weaponized to launch large-scale distributed denial-of-service attacks against critical infrastructure and online services.
Other alleged co-conspirators linked to the broader Snowflake data theft conspiracy are facing separate legal battles in various jurisdictions. Conor Riley Moucka, operating under the alias “Judische” out of Kitchener, Ontario, was arrested in 2024 and entered a guilty plea in August 2026. Meanwhile, John Erin Binns, an American citizen currently residing in Turkey, remains wanted by authorities. Binns is also implicated in a massive 2021 data breach at T-Mobile that exposed the personal identifying information of at least 76 million customers.
As the extortion scheme unraveled, Kiberphant0m engaged in increasingly erratic and dangerous behavior, including attempts to re-extort victimized companies by threatening to disclose classified national security secrets. Immediately following the arrest of Moucka—and despite the fact that AT&T had already paid the extortion syndicate a ransom of approximately $370,000 worth of Bitcoin—Kiberphant0m published what he claimed were the AT&T call logs belonging to then President-elect Donald Trump and then Vice President Kamala Harris. Alongside these political targets, he also leaked documents and schematics allegedly stolen from the U.S. National Security Agency.
The involvement of an active-duty soldier with a secret security clearance triggered an immediate, high-priority response from military and federal law enforcement agencies. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service—the criminal investigative arm of the U.S. Department of Defense Office of Inspector General—explained the gravity of the situation when the initial intelligence landed on investigators’ desks. Upon learning that a service member with security clearance was allegedly fabricating hacking tools and trafficking in stolen data, DCIS initiated a joint task force alongside the Federal Bureau of Investigation, the Army Criminal Investigative Division, and the U.S. Secret Service.
According to Russell, discovering an active-duty insider threat of this magnitude is a rare and alarming occurrence. The unique nature of the threat—involving a military insider with privileged access—created immediate concern among partner agencies because the full extent of the compromised systems and potential intelligence leaks remained entirely unknown during the initial phases of the investigation.
Complications continued to mount even after Wagenius was taken into custody. A sentencing memo filed by federal prosecutors in Seattle revealed that while Wagenius cooperated promptly after his guilty plea, he was later caught attempting to probe and find security vulnerabilities within the computer networks of the federal Bureau of Prisons while incarcerated and awaiting his sentencing hearing. Government documents detail that while awaiting his legal fate, Wagenius repeatedly violated BOP computer use policies by orchestrating unauthorized technical inquiries.
Records indicate that in September 2025, Wagenius used another inmate’s email system to prompt a commercial artificial intelligence tool for specific technical exploits. He allegedly requested information regarding privilege escalation vulnerabilities and bypasses for Windows 10 Enterprise, alongside explicit demands for real-world working scripts with un-omitted code. Less than a week later, utilizing a different inmate’s email account, he instructed an AI tool to provide step-by-step instructions and potential code for CVE-2023-45208, a command injection vulnerability affecting D-Link networking devices.
During the same timeframe, Wagenius allegedly queried the AI system on how to construct a makeshift radio antenna inside a prison environment using commissary items and readily available tools to extend radio reception. Prosecutors also noted that he researched methods for escaping a correctional facility. In several of these instances, Wagenius attempted to bypass artificial intelligence safety filters by framing his malicious queries as background research for a book he claimed to be writing, a classic technique known as prompt injection designed to trick AI safety guardrails into outputting functional exploit code.
While federal prosecutors confirmed they found no evidence that Wagenius successfully deployed or utilized these researched vulnerabilities against the prison system’s internal networks—and noted that Wagenius claimed he was merely researching potential weaknesses to report them to prison authorities—the behavior underscored his persistent technical fixation.
Despite the monumental scale of data exfiltrated from AT&T and other telecommunications giants, financial records and prosecutorial findings revealed a stark reality: Wagenius’s high-profile extortion efforts were remarkably unsuccessful from a monetary standpoint. The government’s sentencing memo indicated that despite compromising data for over 100 million individuals, Wagenius netted a grand total of only about $1,500 from selling his stolen troves.
The sentencing memo encapsulated the paradoxical nature of the case, concluding that while Wagenius ultimately proved unsuccessful as a profitable cybercriminal, his reckless actions intentionally caused profound and widespread harm to individual consumers, major corporate entities, and the security interests of the United States government.